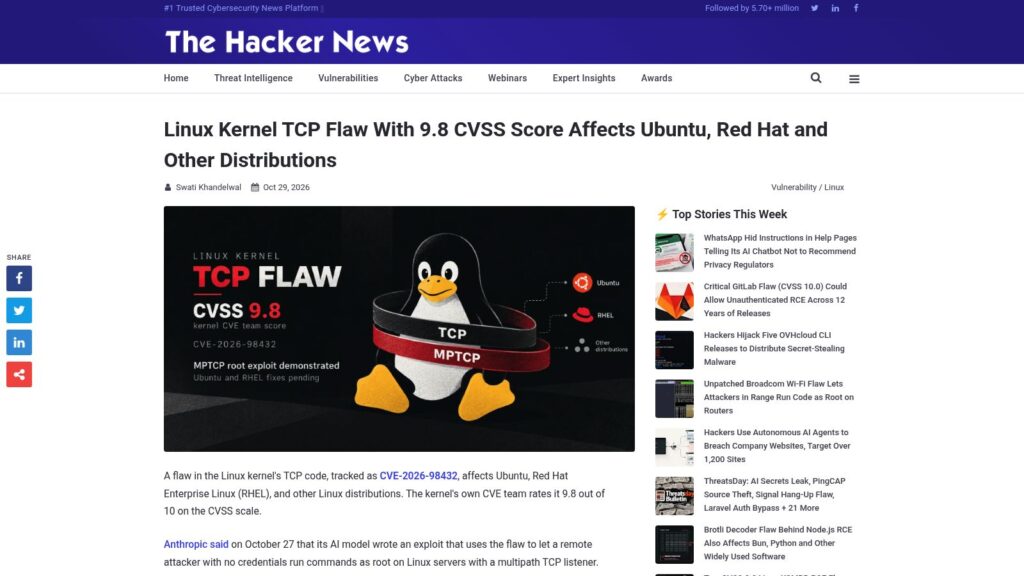
A critical race condition vulnerability (CVE-2026-98432) in the Linux kernel’s TCP code allows remote attackers to execute commands as root, affecting Ubuntu, Red Hat, and other distributions with a CVSS score of 9.8 assigned by the kernel’s CVE team. While Debian, Oracle Linux, SUSE, and Amazon Linux have released patches, Ubuntu and Red Hat have yet to provide fixed kernels, and the flaw primarily exploits the multipath TCP feature, with recommendations to update to patched kernel versions where available. Anthropic’s AI-generated exploit demonstrates how an attacker can leak kernel memory addresses and gain root access, highlighting the urgency to apply updates once released.
https://thehackernews.com/2026/10/linux-kernel-tcp-flaw-with-98-cvss.html