phishing

Attackers Abuse ChatGPT Custom GPTs to Deliver RAT Via ClickFix Lures
Threat actors are abusing ChatGPT's Custom GPT feature to trick users into visiting malicious sites that deploy ClickFix lures, leading to the download of a remote access trojan (RAT). The attack starts with sponsored search results directing victims to attacker-created Custom GPTs, which provide links to fake Cloudflare CAPTCHA pages that execute PowerShell commands to install malware using DLL sideloading and evasion techniques. Over 40 users have been infected so far in this campaign, highlighting continued exploitation of trusted AI platforms for social engineering and malware delivery.

https://thehackernews.com/2026/09/attackers-abuse-chatgpt-custom-gpts-to.html
AI-Powered Phishing Platform EvilTokens Disrupted by Microsoft

Microsoft has disrupted EvilTokens, an AI-driven phishing platform responsible for compromising over 12,000 email accounts across 10,000 organizations worldwide through device code phishing. The platform used AI to craft targeted phishing messages, manage compromised inboxes, and optimize attacks, operating as a paid service until Microsoft seized 50 related websites, disabled 150 domains, and helped arrest two suspects in the UK.

https://www.securityweek.com/ai-powered-phishing-platform-eviltokens-disrupted-by-microsoft/

How Device Code Phishing Gives Scammers Access to Your Account

Device code phishing exploits the OAuth 2.0 Device Authorization Grant by tricking victims into entering a legitimate short code on a real sign-in page, unknowingly approving a scammer's sign-in request and granting them access to the victim’s account. This attack bypasses typical security measures such as multifactor authentication because the victim themselves authorizes the sign-in, allowing attackers to obtain authentication tokens to access emails, files, or other services depending on granted permissions. Users should be wary of unexpected requests to enter sign-in codes purportedly for meetings or documents and verify legitimate device sign-ins, while monitoring account activity if a scam is suspected.

https://www.malwarebytes.com/blog/how-to/2026/09/how-device-code-phishing-gives-scammers-access-to-your-account

N0va Phishkit Targets US and EU Businesses: a New Challenge for Identity Security

The N0va phishkit is conducting sophisticated phishing campaigns targeting organizations across North America and Europe, leveraging trusted business platforms and legitimate authentication flows to steal access tokens and gain single sign-on entry to corporate resources. This identity compromise risks financial loss, sensitive data exposure, operational disruption, and reputational damage, especially in high-risk sectors such as government, healthcare, and technology. Security teams are advised to use advanced threat intelligence tools and behavioral analysis to detect, contextualize, and respond swiftly to N0va-related attacks to minimize impact and contain breaches effectively.

https://thehackernews.com/2026/09/n0va-phishkit-targets-us-and-eu.html

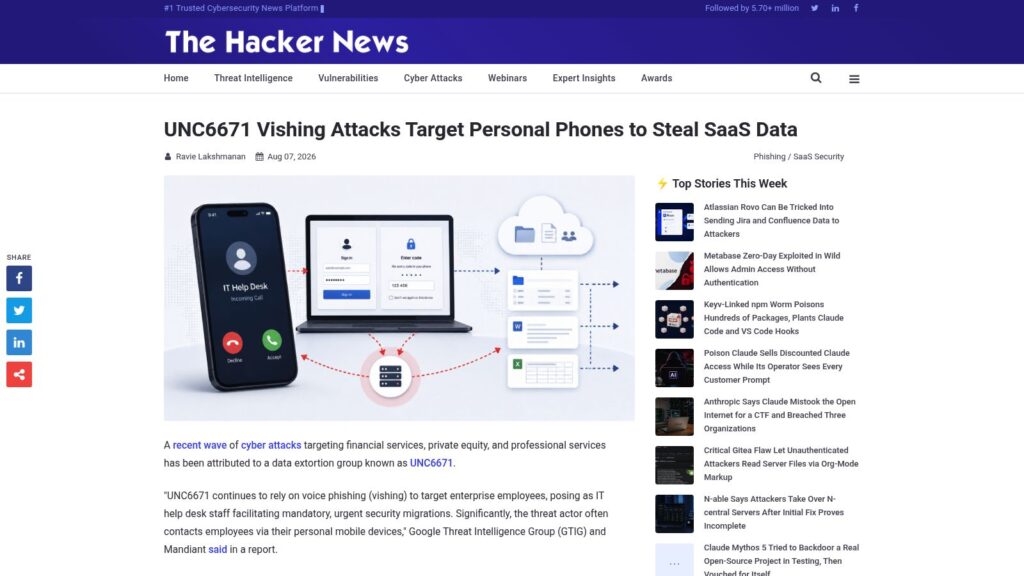
UNC6671 Vishing Attacks Target Personal Phones to Steal SaaS Data

The threat actor group UNC6671 has been conducting vishing attacks targeting personal mobile phones of enterprise employees to steal SaaS credentials and exfiltrate data from cloud environments like Microsoft 365 and Okta. Using social engineering, spoofed help desk calls, and adversary-in-the-middle phishing portals, they intercept login credentials and multi-factor authentication tokens to gain persistent access and lateral movement across SaaS ecosystems. The group operates multiple extortion brands, demands ransoms often negotiated down to hundreds of thousands of dollars, and highlights the necessity of phishing-resistant MFA and vigilant identity provider monitoring to mitigate such risks.

https://thehackernews.com/2026/08/unc6671-vishing-attacks-target-personal.html

Microsoft Teams Vishing Attacks Lead to Chaos Ransomware Attacks

Threat actors are conducting vishing attacks via Microsoft Teams by impersonating IT support staff to gain remote access to corporate devices, leading to Chaos ransomware infections in North American organizations. The campaign, tracked as STAC4749 by Sophos, targeted mainly Canadian and US companies across multiple sectors, using fake IT domains and remote support tools like Microsoft Quick Assist and RemSupp to deploy backdoors and achieve persistence before deploying ransomware. Some attacks resulted in data theft and rapid ransomware encryption within 17 hours of initial access.

https://www.bleepingcomputer.com/news/security/microsoft-teams-vishing-attacks-lead-to-chaos-ransomware-attacks/

Attackers Are Turning Microsoft’s Trusted Login System Into Their Latest Phishing Weapon

Attackers are exploiting Microsoft’s legitimate login system by directing victims to real Microsoft sign-in pages to grant permissions to malicious apps, enabling phishing campaigns to bypass traditional detection. This method, observed in over 200 phishing emails targeting around 120 organizations worldwide, allows attackers to access email, files, Teams, SharePoint, OneDrive, and calendars within the victim’s Microsoft 365 environment. The campaign emphasizes the growing threat of abuse of trusted authentication flows and highlights the need for vigilance despite appearances of legitimate Microsoft login prompts.

https://blog.checkpoint.com/email-security/attackers-are-turning-microsofts-trusted-login-system-into-their-latest-phishing-weapon/

New Ghost Phishing Wave Is Breaking Traditional Email Security

A new “ghost phishing” campaign called EvilTokens uses encrypted phishing pages that only decrypt and display malicious content within the victim's browser, bypassing traditional email and URL security checks. This technique primarily targets Microsoft 365 users across industries in the US and Europe, enabling account takeover without stealing passwords directly and complicating detection and response efforts. Security teams are urged to adopt browser-level sandboxing tools that reveal hidden phishing behaviors in real time to shorten exposure windows and improve incident containment.

https://thehackernews.com/2026/07/new-ghost-phishing-wave-is-breaking.html

Entra Passkey Enrollment Vishing Targets Microsoft 365 Users

A threat actor tracked as O-UNC-066 has been conducting vishing campaigns targeting Microsoft 365 users across multiple industries by impersonating Microsoft Entra passkey enrollment processes. Attackers use phishing sites mimicking legitimate enrollment portals to trick victims into registering passkeys controlled by the attacker, enabling account takeover and data theft from SharePoint and OneDrive. The extortion group Pink, associated with this campaign, exfiltrates stolen data and pressures victims for ransom payments.

https://www.bleepingcomputer.com/news/security/entra-passkey-enrollment-vishing-targets-microsoft-365-users/

When Checking the URL Isn’t Enough: Phishing Via the Microsoft Identity Platform

The article discusses a sophisticated phishing technique that abuses the Microsoft identity platform’s device code flow, making it difficult to detect purely by checking URLs. Attackers leverage this method to bypass traditional phishing defenses by exploiting trusted Microsoft OAuth authentication processes, highlighting the need for enhanced vigilance and security measures beyond URL inspection to defend against such threats.

https://securelist.com/microsoft-device-code-phishing-attack/120350/

The Booking.com Phishing Campaign Targeting Hotels and Customers

Since January 2026, a phishing campaign has targeted hotels and their customers by impersonating Booking.com to conduct financial fraud. The attack unfolds in three stages: initial phishing emails sent to hotel partners to harvest credentials via a partner phishing kit, followed by customer-targeted phishing to steal financial information, delivered in part through WhatsApp. The campaign uses domain spoofing, typosquatting, and advanced evasion techniques such as user fingerprinting to avoid detection, posing significant risks to the hospitality sector.

https://www.bridewell.com/insights/blogs/detail/the-booking.com-phishing-campaign-targeting-hotels-and-customers

Cybersecurity Firms Targeted by Fraudulent OpenAI Organization Invites

Threat actors have been creating fraudulent OpenAI ChatGPT organizations impersonating legitimate companies, such as Push Security, to send legitimate-looking invitations to targeted employees with the goal of tricking them into sharing sensitive company information. These attacker-controlled tenants assign invitees administrative privileges and include payment methods to appear credible, enabling them to collect confidential data submitted within the workspace. Security experts warn this reflects a growing tactic of abusing legitimate SaaS invitation systems to bypass email security measures and recommend staff training and monitoring of SaaS memberships to mitigate risks.

https://www.bleepingcomputer.com/news/security/cybersecurity-firms-targeted-by-fraudulent-openai-organization-invites/

Mirage2FA Phishing Kit Uses HTML Smuggling to Steal Microsoft 365 Credentials

Researchers at Fortra uncovered Mirage2FA, a phishing kit that uses HTML smuggling and obfuscated JavaScript to deploy fake Microsoft 365 login pages, tricking users into submitting credentials and multi-factor authentication details. The campaign employs business-themed lures and short-lived domains to carry out Microsoft 365 account takeovers, potentially exposing email, files, Teams messages, and other cloud resources. Users affected are advised to reset passwords, revoke sessions, review MFA methods, and check for unauthorized mailbox access.

https://www.helpnetsecurity.com/2026/06/26/mirage2fa-phishing-kit-microsoft-365-html-smuggling/

A Backdoor in a LinkedIn Job Offer

A LinkedIn message from a recruiter at a crypto startup led Roman Imankulov to analyze a suspicious GitHub repo purportedly needing a Node modules review. The repo contained a hidden backdoor in a test file that executed arbitrary code fetched from a remote server whenever dependencies were installed, triggered by an npm lifecycle script. The repo and recruiter used stolen identities, highlighting the risk of supply-chain and social engineering attacks via seemingly legitimate job offers.

https://roman.pt/posts/linkedin-backdoor/

These Convincing Copyright Notices Are Designed to Steal Google Logins

A new phishing scam targets Chrome extension developers with fake copyright removal notices designed to steal Google login credentials. The scam uses publicly available extension information to create convincing personalized warnings and a fake Google sign-in window, pressuring victims to enter their credentials before a fabricated deadline. Developers are advised to verify warnings only through their Chrome Web Store dashboard and to safeguard accounts with strong authentication and security software.

https://www.malwarebytes.com/blog/threat-intel/2026/06/these-convincing-copyright-notices-are-designed-to-steal-google-logins

Scroll to Top