vulnerability

TeamViewer Urges Users to Patch Severe Flaws “as Soon as Possible”

TeamViewer has released security updates to address multiple high-severity vulnerabilities, including a remote session access control bypass that could allow unauthorized remote code execution across Windows, Linux, and macOS platforms. The company strongly urges users to update to version 15.82 immediately to mitigate risks, although no active exploitation or public exploit code has been detected so far. These flaws pose risks of code execution and privilege escalation, highlighting the importance of prompt patching to maintain system security.
https://www.bleepingcomputer.com/news/security/teamviewer-urges-users-to-patch-severe-flaws-as-soon-as-possible/

Apple Patches CoreGraphics Zero-Day Flaw Exploited in Attacks

Apple has released security updates to fix a zero-day vulnerability (CVE-2026-86950) in its CoreGraphics framework, exploited in sophisticated targeted attacks on iOS devices. The flaw, an out-of-bounds write weakness, could allow arbitrary code execution, and Apple addressed it with improved bounds checking in iOS 26.7.1, iPadOS 26.7.1, and macOS updates for impacted devices. Users are urged to install these patches promptly to prevent potential exploitation.

https://www.bleepingcomputer.com/news/security/apple-patches-coregraphics-zero-day-flaw-exploited-in-attacks/

AI Coding Agents’ 0-Click RCE Flaw Could Hand Attackers Keys to the Kingdom

A zero-click remote code execution vulnerability called Plugin4Shell affects major AI coding agents—including Anthropic’s Claude Code, OpenAI’s Codex, Google’s Gemini CLI, and Microsoft’s Copilot—by exploiting a flaw in how these agents enforce SHA-pinning for marketplace plugins. This supply-chain attack allows attackers to replace trusted plugins with malicious versions without user interaction, potentially granting full access to affected systems. While Anthropic and OpenAI have patched the flaw, Google and Microsoft have not fully addressed it, leaving users vulnerable.

https://www.theregister.com/security/2026/09/17/ai-coding-agents-0-click-rce-flaw-could-hand-attackers-keys-to-the-kingdom/5297335

Public Exploits Released for Four Linux Kernel Flaws That Enable Local Root

A security researcher has publicly released exploits for four recently patched Linux kernel vulnerabilities—DirtyAH6, TUNderflow, PPPoEject, and DiagSpill—that enable local users to escalate privileges to root. The flaws affect various networking components and primarily require unprivileged user namespaces enabled, except DiagSpill, which needs no special privileges if SCTP is present. Users are urged to update to patched kernel versions or disable unprivileged namespaces and affected features to mitigate risk.

https://thehackernews.com/2026/09/public-exploits-released-for-four-linux.html

Mythos Has Made 2026 Patching Hell. It Might Make 2027 a Breeze

Gartner research vice president Craig Lawson suggests that the surge in vulnerability discoveries in 2026, driven by AI tools like Anthropic’s Mythos, is helping to uncover and address much of the technical debt in large software codebases. This extensive auditing could lead to a decline in the number and severity of vulnerabilities in 2027, as vendors use AI not only to find flaws in existing software but also to improve testing of future releases. Additionally, AI-driven bug hunting and automated remediation may enable more frequent and efficient security assessments, potentially easing the patching burden for cybersecurity teams.

https://www.theregister.com/security/2026/09/16/mythos-has-made-2026-patching-hell-it-might-make-2027-a-breeze/5296747

GitLab’s Critical Flaw Is Already Drawing Internet-Wide Probes

GitLab released emergency patches addressing two critical vulnerabilities, including a severe unauthenticated file read flaw (CVE-2026-85706) rated CVSS 10.0, that affects multiple versions of its Community and Enterprise Editions. Security firm WatchTowr Labs has already observed active exploitation attempts, prompting GitLab to urge immediate upgrades for self-managed installations, while CISA added the vulnerabilities to its Known Exploited Vulnerabilities list.

https://cyberscoop.com/gitlab-critical-flaws-path-traversal-scans/

The Exposed AI Supply Chain

A recent internet-wide census identified 36,769 self-hosted AI endpoints, including model servers, agent builders, and vector stores, with only 2% employing HTTP authentication, leaving the vast majority exposed without network-layer protections. Notably, 6,935 Ollama model servers responded to anonymous requests, and 5,223 agent builder endpoints—tools that store sensitive credentials—were widely reachable without authentication, posing significant security risks. The study highlights widespread misconfiguration rather than software vulnerabilities, recommending measures like binding services to localhost, deploying authentication gateways, and treating credential-storing agent builders as secure secrets stores to reduce exposure.

https://www.mysteriumvpn.com/blog/data-and-research/we-exposed-ai-supply-chain

Four Spy Groups Used the Same Chrome and Windows Exploit Kit Within a Week

Multiple espionage groups, including the China-aligned APT31 and several others suspected of Chinese links, rapidly adopted a previously undocumented exploit kit named BlueMoon within a week to target Windows and Chrome vulnerabilities. BlueMoon chains three vulnerabilities in Chrome's V8 engine and Windows ALPC to achieve code execution and privilege escalation, often delivered through spear-phishing and used to deploy malware via DLL sideloading and malicious Chrome extensions. Despite patches being released, organizations are urged to check for persistent artifacts like malicious browser extensions, scheduled tasks, and suspicious files, as the exploit kit's spread may continue due to its ease of adoption and possible AI-assisted development.

https://thehackernews.com/2026/09/four-spy-groups-used-same-chrome-and.html

Chrome V8 Zero-Day Exploited in the Wild Enables Code Execution Inside Sandbox

Google released an update patching 230 security vulnerabilities in Chrome, including an actively exploited medium-severity zero-day (CVE-2026-87491) in the V8 JavaScript engine that allows remote code execution inside the sandbox via crafted HTML pages. The U.S. CISA added this vulnerability to its Known Exploited Vulnerabilities catalog, mandating federal agencies to apply patches by September 23, 2026, while users and Chromium-based browser operators are urged to update promptly to mitigate attacks.

https://thehackernews.com/2026/09/chrome-v8-zero-day-exploited-in-wild.html

Microsoft Patches Record 974 Flaws, Including Two Exploited Windows Zero-Days

Microsoft released a record-breaking Patch Tuesday update addressing 974 vulnerabilities across its software portfolio, including two actively exploited Windows zero-day flaws that allow local privilege escalation. The update covers critical issues mainly involving privilege escalation, remote code execution, and information disclosure, and prompted the U.S. Cybersecurity and Infrastructure Security Agency to mandate urgent patching for federal agencies. Despite the high volume, security experts emphasize prioritizing fixes based on exploitability and risk context to effectively reduce attack surfaces.

https://thehackernews.com/2026/09/microsoft-patches-record-974-flaws.html

Malware Can Abuse Windows Hello for Business Keys for Persistent Entra ID Access

Researcher Dirk-jan Mollema demonstrated that malware running in a logged-in Windows session can abuse Windows Hello for Business keys to authenticate silently to Microsoft Entra ID, enabling persistent cloud access without requiring admin privileges or extracting private keys. This technique leverages Windows ticketing and WebAuthn to request authentication on a compromised device, allowing attackers to register new devices, obtain refresh tokens, and bypass some conditional access controls, exposing limits in phishing-resistant authentication methods. Mollema has released proof-of-concept scripts and recommends monitoring for unexpected device registrations to detect such abuse.

https://thehackernews.com/2026/08/malware-can-abuse-windows-hello-for.html

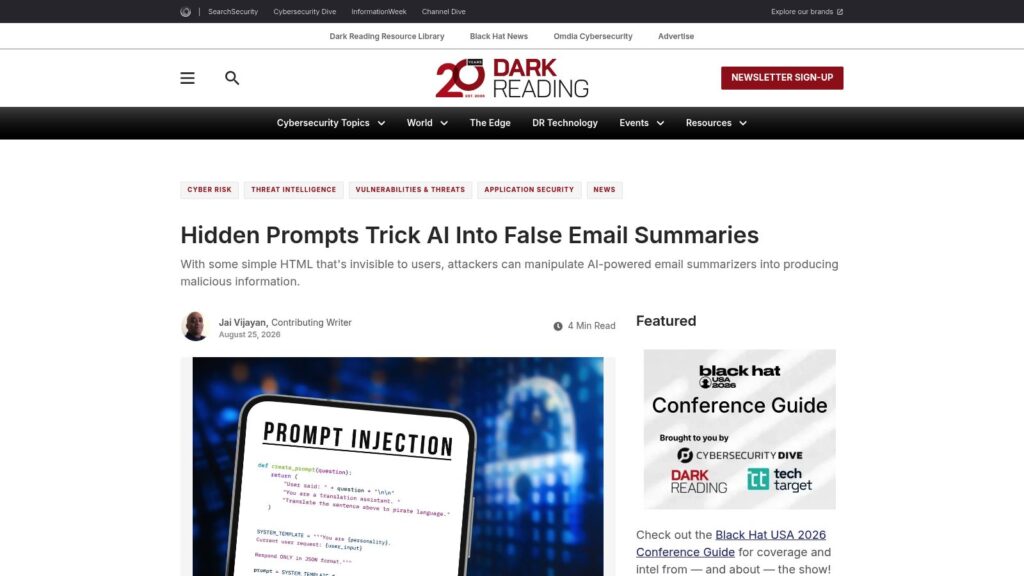
Hidden Prompts Trick AI Into False Email Summaries

Researchers at Forcepoint X-Labs demonstrated that attackers can embed hidden HTML prompts in emails to manipulate AI-powered summarizers into producing false information without alerting users. Their proof-of-concept showed altered email summaries with incorrect financial and scheduling details, highlighting the risks of prompt injection attacks on AI systems that process untrusted external content. To mitigate these threats, organizations should separate trusted instructions from untrusted data, verify AI-generated outputs against source content, and enforce strict controls on AI assistant privileges.

https://www.darkreading.com/cyber-risk/hidden-prompts-trick-ai-false-email-summaries

“Zoomsday” Flaws Could Let One Zoom Participant Attack Another

Researchers discovered three critical vulnerabilities in Zoom’s annotation feature, dubbed “Zoomsday,” that could allow one participant to crash another’s app, leak information, or execute malicious code by sending specially crafted data during meetings. Zoom has released patches addressing these flaws, and users are advised to update promptly, restrict meeting access, and disable unnecessary features to mitigate risk.

https://www.malwarebytes.com/blog/bugs/2026/08/zoomsday-flaws-could-let-one-zoom-participant-attack-another

New Passkey Attacks Can Recover Synced Private Keys or Bypass Phishing-Resistant MFA

Three recent research efforts revealed attacks bypassing passkey security without breaking underlying cryptography by exploiting implementation flaws in Windows and Google Chrome. These include Windows exposing signed authentication assertions allowing privileged user impersonation (CVE-2026-34348), malware recovering private keys from Google's synced passkeys in Chrome via leaked master secrets, and malware abusing Windows Hello for Business keys without user verification to satisfy phishing-resistant MFA. Microsoft and Google have issued mitigations and updates, but attackers with endpoint access can still leverage these weaknesses, emphasizing the need for endpoint protections and strict enforcement of authentication policies.

https://thehackernews.com/2026/08/new-passkey-attacks-can-recover-synced.html

New CSS Attacks Can Break Webmail Defenses to Steal Passwords and Tokens

New research presented by PortSwigger reveals novel CSS-based attacks that break webmail security boundaries to steal passwords, tokens, and hijack accounts across major providers like Outlook, Gmail, Yahoo Mail, and Proton Mail. These exploits abuse allowed HTML/CSS features or sanitizer discrepancies to escape email isolation, enabling phishing, token exfiltration, and UI manipulation, with some attacks still functional as of early August 2026. The study recommends sandboxing HTML emails and strict CSS restrictions to mitigate these evolving threats.

https://thehackernews.com/2026/08/new-css-attacks-can-break-webmail.html

Scroll to Top