Old Bitly Links Hijacked in Burger King, McDonald’s and Trump Tweets
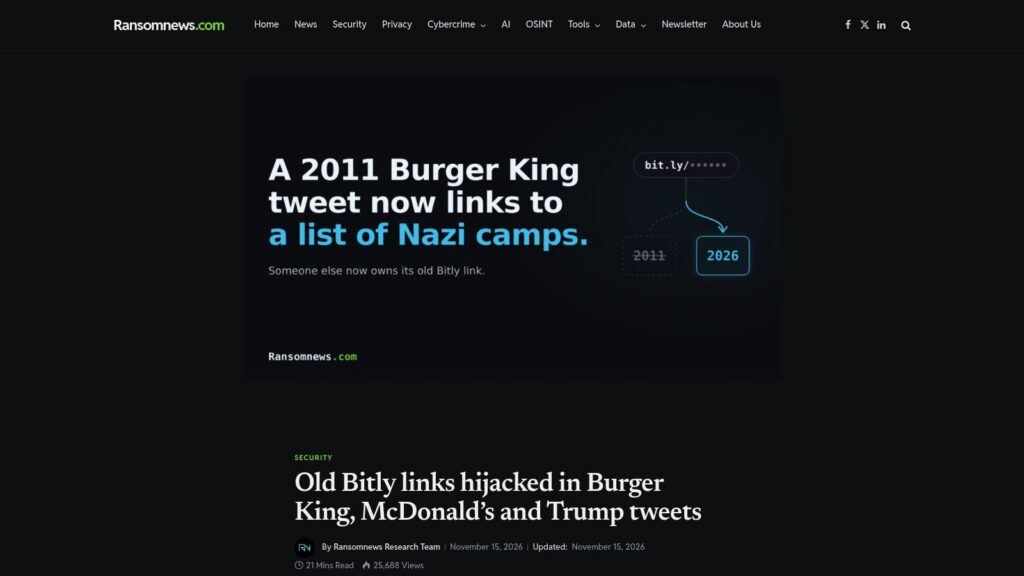
Old Bitly short links embedded in historical tweets from Burger King, McDonald’s, Donald Trump, and other prominent accounts were hijacked when their original shortened URLs expired and were re-registered by attackers who redirected them to unrelated, sometimes controversial content. Bitly confirmed a security issue that allowed bad actors to repurpose these inactive links, suspended the accounts involved, and disabled affected links, but nearly half of the examined Trump-era links remain active with altered destinations. This exploitation poses risks as old verified posts with replaced links can mislead users, highlighting the need for organizations to audit and secure legacy short links.

https://ransomnews.com/burger-king-tweet-bitly-link-hijack-2026/
Windows 0-Day Dropped by Disgruntled Researcher Hands Hackers System Rights

A researcher known as Nightmare Eclipse has publicly disclosed a Windows zero-day vulnerability called SignDrop that allows local users to escalate privileges to full System rights by exploiting the Common Log File System (CLFS) and Windows Defender. This flaw abuses Windows Defender’s file operations and symbolic links to create files with System privileges, effectively bypassing antivirus self-protection mechanisms. Microsoft is investigating the issue, noting no evidence of exploitation in the wild, and Defender reportedly blocks attempts, while the vulnerability affects certain 26H2 Windows versions with specific CLFS authentication modes enabled.

https://arstechnica.com/security/2026/11/windows-0-day-dropped-by-disgruntled-researcher-hands-hackers-system-rights/

PostgreSQL Patches 52 Flaws, Including 22-Year-Old Bug Enabling Authenticated RCE

PostgreSQL has released updates fixing 52 security vulnerabilities, including a 22-year-old type confusion bug (CVE-2026-6460) that allows authenticated users with object creation privileges to execute code on the server with the operating system user’s rights. The patch adds version checks to prevent this flaw, and full mitigation requires rebuilding all C-language extensions; administrators are urged to update to the latest minor releases and update client tools accordingly. No attacks exploiting this vulnerability have been reported so far, and the flaw affects all versions prior to 18.7, 17.12, 16.16, 15.20, and 14.25.

https://thehackernews.com/2026/11/postgresql-patches-52-flaws-including.html

How AI Revived a Stalled Attack on a U.S. Retailer

In September 2026, attackers targeting a U.S. retail organization initially used manually typed commands that were consistently blocked, but then switched to AI-assisted, complex PowerShell scripts that enabled rapid credential harvesting and lateral movement across servers within minutes. The AI-generated commands featured structured output, error handling, and explanatory comments, allowing the attackers to quickly exploit SolarWinds Orion monitoring software to move laterally using Erlang RPC calls, reflecting an operator relaying information through an AI tool rather than autonomous malware. This case is part of a broader surge in AI-assisted attacks that accelerate attackers’ ability to adapt and persist using known tactics without introducing new techniques.

https://www.security.com/threat-intelligence/ai-assisted-attack-us-retailer

Binance Warns of iOS Flaw That Could Leak Crypto Wallet Secrets

Binance has warned of a vulnerability in iOS versions 26.7.1, 27.0.1, and 27.2 that could allow malicious third-party apps to access private files from other apps, risking exposure of cryptocurrency seed phrases, private keys, and login credentials. The flaw, known as “worse_query,” enables a sandbox escape allowing cross-app data access, with a public proof-of-concept exploit available via a sideloaded app called WQ Files. Apple released security updates on November 9 to address several flaws, but it remains unclear if these fully mitigate the specific issue Binance highlighted.

https://www.bleepingcomputer.com/news/security/binance-warns-of-ios-flaw-that-could-leak-crypto-wallet-secrets/

Critical Apache HTTP/2 Flaw Could Let Unauthenticated Attackers Execute Code Remotely

A critical vulnerability (CVE-2026-119618) in the Apache HTTP Server’s HTTP/2 module, mod_http2, allows unauthenticated remote attackers to execute code on affected servers running versions 2.4.55 through 2.4.70. The flaw, fixed in version 2.4.71, requires HTTP/2 to be enabled and has a CVSS score of 9.8; administrators are urged to update or disable HTTP/2 protocols to mitigate the risk.

https://thehackernews.com/2026/11/critical-apache-http2-flaw-could-let.html

After 7-Months, Glasswing Overwelms Maintainers with Underwhelming Findings

Seven months into Anthropic’s Project Glasswing, VulnCheck has tracked 442 attributed CVEs—only about 0.5% of the total CVEs published this year—with just two exploited in the wild and a low remediation rate of 217 fixes out of nearly 38,000 findings. The project’s vulnerability reporting has shifted much of the triage burden onto open source maintainers, exemplified by curl rejecting over half of Anthropic’s OSS Scanner reports as false positives or low severity, casting doubt on the claimed 94.2% true positive rate and the project’s overall effectiveness in identifying critical, actionable vulnerabilities.

https://www.vulncheck.com/blog/anthropic-glasswing-november-update

N-able Disables Cloud Services Following Disclosure of “Able2Shell” Exploit Chains

N-able temporarily took its N-central hosted environments offline after a security researcher disclosed 33 critical vulnerabilities, collectively named “Able2Shell,” affecting remote monitoring and management servers. On November 10, N-able released a critical security update (N-central 2026.4 HF2) addressing these flaws, which include remote code execution and privilege escalation risks, and restored hosted services after applying patches; customers with on-premises deployments are urged to upgrade immediately. Despite scanning activity related to proof-of-concept exploits, N-able and Huntress have not observed active exploitation in customer environments.

https://www.huntress.com/blog/n-able-disables-cloud-services-following-disclosure-of-able2shell-exploit-chains

Linus Torvalds Sees Signs AI-prompted Patch Flood Has Peaked

Linux kernel lead Linus Torvalds noted in his weekly update that the influx of AI-driven bug reports and patches may have peaked, citing faster fixes than new reports in the eBPF subsystem. This improvement follows a surge in vulnerability discoveries driven by AI tools like Anthropic’s Mythos, which caused record numbers of patches across major projects, raising challenges for IT teams. Torvalds suggested this trend could signal a turning point where developers start to catch up with AI-identified flaws in the large Linux kernel codebase.

https://www.theregister.com/security/2026/11/09/linus-torvalds-sees-signs-ai-prompted-patch-flood-has-peaked/5308345

Office Party: Vulnerability in Anthropic’s Office Skills

Researchers found a vulnerability in Anthropic’s official DOCX, PPTX, and XLSX AI skills that allows malicious code execution on Linux machines by exploiting a fixed, unverified file path used to preload a shared library. This flaw lets an attacker plant a malicious library in a shared temp directory, which the skills then load via LD_PRELOAD when running LibreOffice, executing attacker code with user privileges. Despite reporting the issue to Anthropic, the vendor has not changed the vulnerable code, highlighting that even trusted official AI skills can pose security risks and require continuous scrutiny and validation.

https://www.air.security/blog-posts/office-party

Vulnerability That Lets Hackers SSH Into Linux Devices Is Under Active Exploitation

A critical vulnerability known as *sshole allows attackers to gain unauthenticated privileged SSH access to Linux systems that use OpenSSH with the musl library under specific configurations. Exploited actively by threat group GT10, the flaw enables rapid intrusion and installation of a backdoor called TAC Agent, facilitating system control and persistence. OpenSSH has released a fix, and users are urged to update promptly to prevent further compromise.

https://arstechnica.com/security/2026/11/vulnerability-that-lets-hackers-ssh-into-linux-devices-is-under-active-exploitation/

Microsoft Fixes RCE Bug in Windows Paint After Weeks of Confusion

Microsoft patched a remote code execution vulnerability (CVE-2026-83844) in Windows Paint that allowed local attackers to execute code with user interaction. Despite Microsoft disclosing the flaw in mid-October, confusion arose over the availability and details of the fix, which was ultimately deployed via the Microsoft Store in early November. The vulnerability carries a high severity score but requires local access and user action, with no known exploitation reports to date.

https://www.darkreading.com/application-security/microsoft-rce-bug-windows-paint-confusion

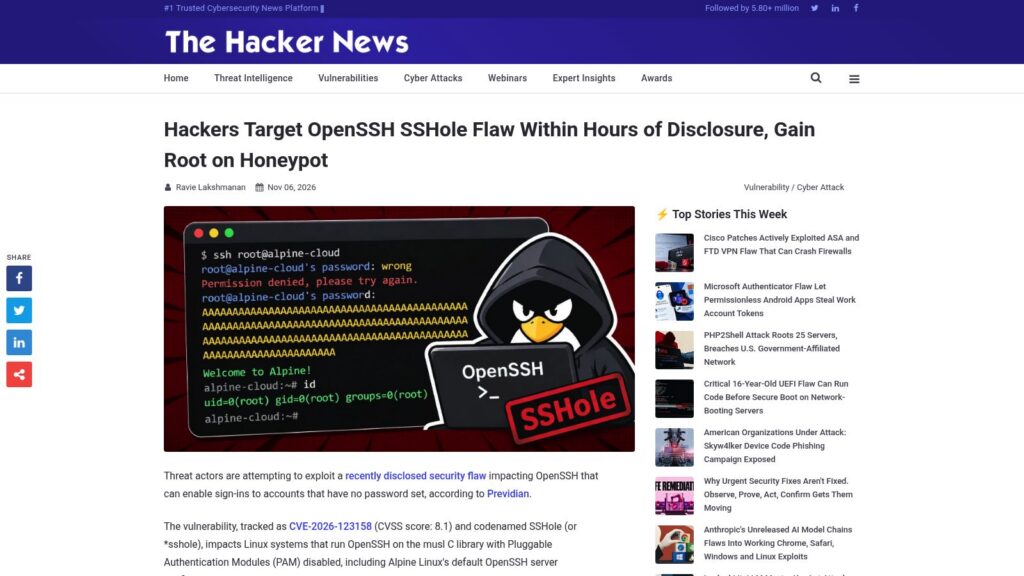
Hackers Target OpenSSH SSHole Flaw Within Hours of Disclosure, Gain Root on Honeypot

Hackers began exploiting a recently disclosed high-severity OpenSSH vulnerability (CVE-2026-123158, “SSHole”) within hours of its publication, targeting Linux systems running OpenSSH on musl libc with PAM disabled, such as Alpine Linux. The flaw allows unauthenticated attackers to bypass password authentication on accounts configured without passwords by sending oversized passwords, granting access with the compromised account’s existing privileges, including root access, as confirmed by successful exploitation on a honeypot. Users are urged to update to OpenSSH 10.6p2 and review login logs for unusual password acceptance on accounts meant to be passwordless.

https://thehackernews.com/2026/11/hackers-exploited-openssh-sshole-flaw.html

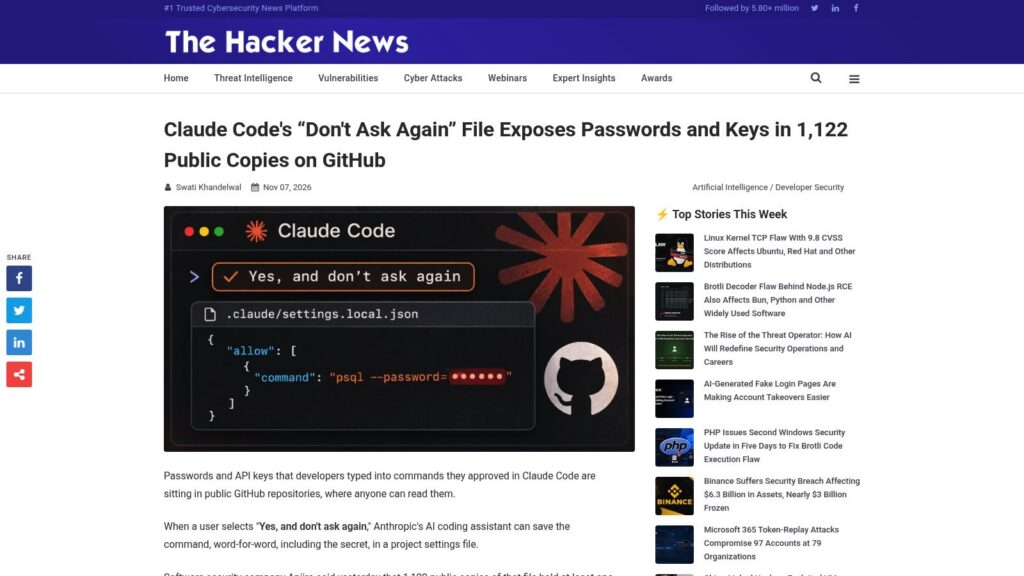
Claude Code’s “Don’t Ask Again” File Exposes Passwords and Keys in 1,122 Public Copies on GitHub

Anthropic’s AI coding assistant Claude Code saves approved shell commands, including embedded passwords and API keys, in a project’s .claude/settings.local.json file, which has been found exposed in 1,122 public GitHub repositories. Security researchers from Apiiro identified 1,379 different secrets in these files, including database passwords, SSH logins, and cloud service keys, often remaining accessible in git history and forks for over 200 days. Developers are advised to rotate all exposed credentials, remove the files from version control, and avoid embedding secrets directly in commands to prevent such leaks.

https://thehackernews.com/2026/11/claude-codes-dont-ask-again-file.html

Microsoft Paint RCE Fix Now Available, but Windows Update Won’t Deliver It

Microsoft has released a fix for CVE-2026-83844, a remote code execution vulnerability in Windows Paint, available exclusively through a Microsoft Store update rather than Windows Update. The patched version is 11.2609.401.0, but many systems may still run older versions, requiring administrators to verify and update each user’s Paint installation via PowerShell commands. Microsoft rates the flaw as important with a CVSS score of 8.1, noting exploitation requires specialized knowledge, and no exploitation has been reported to date.

https://thehackernews.com/2026/11/microsoft-paint-rce-fix-now-available.html

Scroll to Top