windows

ClickFix Attacks Infecting PCs and Macs Are Going Viral

ClickFix attacks have rapidly become widespread on both PCs and Macs by tricking users into pasting and executing malicious commands via fake CAPTCHA prompts on compromised websites. This social engineering exploits users' fatigue with complex web interactions, prompting them to unknowingly run malware without the need for traditional code-signing or heavy infrastructure. Security firms have observed ClickFix variants bypassing protections like macOS Gatekeeper, with attackers increasingly leveraging public services and blockchain for control, making this an enduring and challenging threat to mitigate through technology alone.

https://arstechnica.com/security/2026/09/clickfix-attacks-infecting-pcs-and-macs-are-going-viral/

Four Spy Groups Used the Same Chrome and Windows Exploit Kit Within a Week

Multiple espionage groups, including the China-aligned APT31 and several others suspected of Chinese links, rapidly adopted a previously undocumented exploit kit named BlueMoon within a week to target Windows and Chrome vulnerabilities. BlueMoon chains three vulnerabilities in Chrome's V8 engine and Windows ALPC to achieve code execution and privilege escalation, often delivered through spear-phishing and used to deploy malware via DLL sideloading and malicious Chrome extensions. Despite patches being released, organizations are urged to check for persistent artifacts like malicious browser extensions, scheduled tasks, and suspicious files, as the exploit kit's spread may continue due to its ease of adoption and possible AI-assisted development.

https://thehackernews.com/2026/09/four-spy-groups-used-same-chrome-and.html

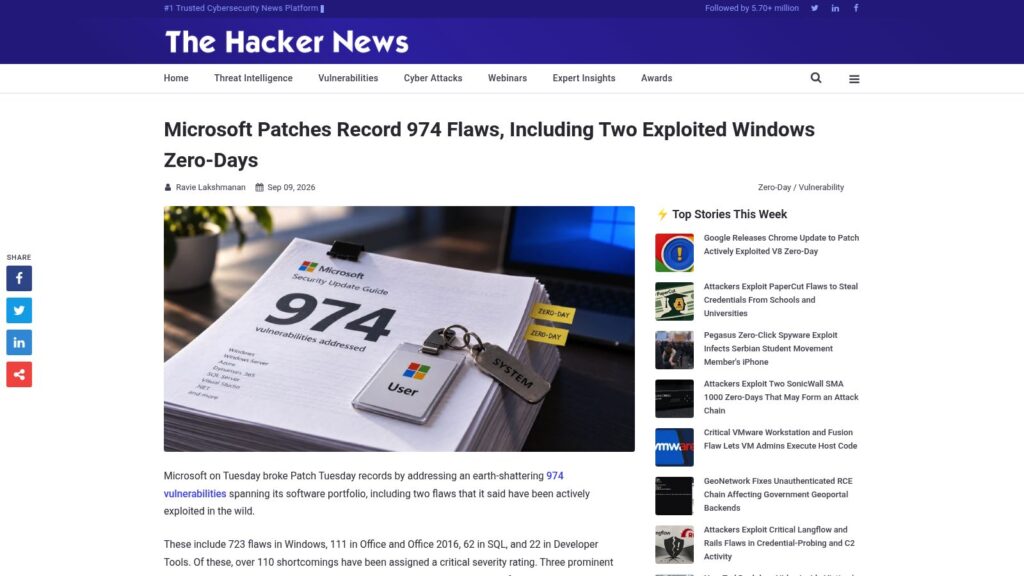
Microsoft Patches Record 974 Flaws, Including Two Exploited Windows Zero-Days

Microsoft released a record-breaking Patch Tuesday update addressing 974 vulnerabilities across its software portfolio, including two actively exploited Windows zero-day flaws that allow local privilege escalation. The update covers critical issues mainly involving privilege escalation, remote code execution, and information disclosure, and prompted the U.S. Cybersecurity and Infrastructure Security Agency to mandate urgent patching for federal agencies. Despite the high volume, security experts emphasize prioritizing fixes based on exploitability and risk context to effectively reduce attack surfaces.

https://thehackernews.com/2026/09/microsoft-patches-record-974-flaws.html

Fake Software Installers Disable Windows Update and Weaken Microsoft Defender

A malware campaign impersonating trusted software vendors via counterfeit download sites targets primarily Chinese-speaking users and organizations, deploying malicious installers that disable Windows Update, weaken Microsoft Defender, and establish persistent access. The attacks, linked to the Chinese threat cluster Silver Fox, use scheduled tasks and PowerShell to evade detection, modify system defenses, and communicate with attacker-controlled command-and-control servers. Victims span multiple sectors including healthcare, manufacturing, and government, while the campaign employs sophisticated tactics like DLL sideloading and code-signing certificate abuse to deliver backdoors such as ValleyRAT.

https://thehackernews.com/2026/09/fake-software-installers-disable.html

You Don’t Want This Sleepwalker Backdoor on Your Windows Machine

Security researcher Dominik Reichel uncovered a sophisticated Windows backdoor called Sleepwalker that resides stealthily in memory, waiting for a specific encrypted network packet to activate its unique 23-instruction command language. Disguised as Microsoft’s dpapi.dll and loaded via side-loading into an ESET Management Agent process, Sleepwalker avoids detection by not initiating outbound traffic or listening on network ports, indicating a well-resourced targeted operation rather than opportunistic malware. While many details about its deployment and operators remain unknown, Reichel has released tools and guidance to detect and mitigate the threat.

https://www.theregister.com/security/2026/08/24/you-dont-want-this-sleepwalker-backdoor-on-your-windows-machine/5292021

Malware Can Abuse Windows Hello for Business Keys for Persistent Entra ID Access

Researcher Dirk-jan Mollema demonstrated that malware running in a logged-in Windows session can abuse Windows Hello for Business keys to authenticate silently to Microsoft Entra ID, enabling persistent cloud access without requiring admin privileges or extracting private keys. This technique leverages Windows ticketing and WebAuthn to request authentication on a compromised device, allowing attackers to register new devices, obtain refresh tokens, and bypass some conditional access controls, exposing limits in phishing-resistant authentication methods. Mollema has released proof-of-concept scripts and recommends monitoring for unexpected device registrations to detect such abuse.

https://thehackernews.com/2026/08/malware-can-abuse-windows-hello-for.html

New Certighost PoC Exploit Lets Attackers Hijack Windows Domains

A proof-of-concept exploit for the Certighost vulnerability (CVE-2026-54121) in Windows Active Directory Certificate Services allows authenticated attackers to impersonate domain controllers and gain domain-level privileges. The flaw exploited a fallback mechanism in certificate enrollment requests, permitting attackers to obtain unauthorized certificates and perform privileged Active Directory operations, including DCSync attacks. Microsoft addressed the issue in the July 2026 Patch Tuesday updates by validating domain controller identities during certificate requests, and administrators are urged to apply these patches promptly.

https://www.bleepingcomputer.com/news/security/new-certighost-poc-exploit-lets-attackers-hijack-windows-domains/

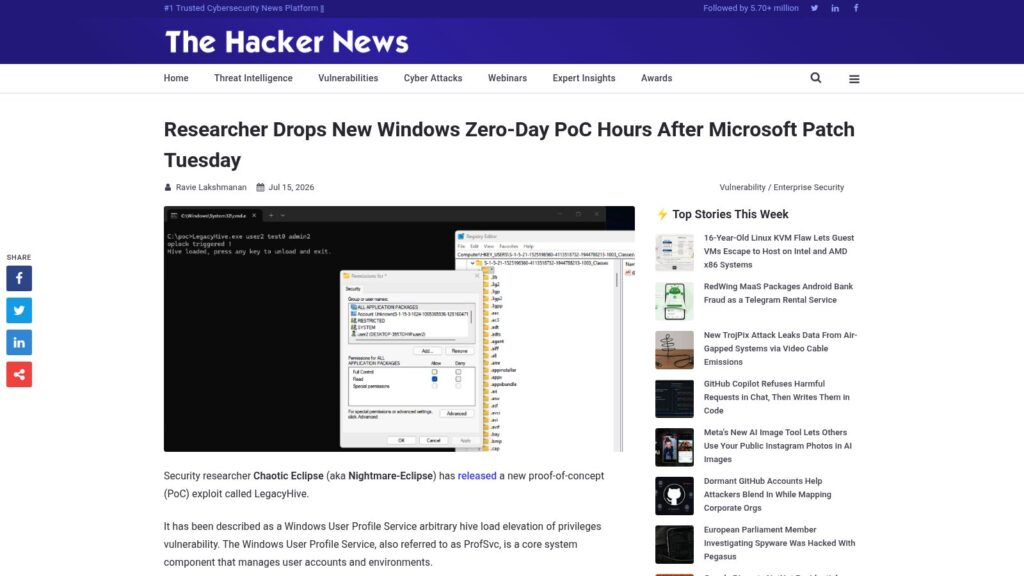
Researcher Drops New Windows Zero-Day PoC Hours After Microsoft Patch Tuesday

Security researcher Chaotic Eclipse released a new proof-of-concept exploit called LegacyHive, which leverages a Windows User Profile Service vulnerability to achieve arbitrary hive load elevation of privileges. The exploit works on all supported Windows versions, including those patched in the latest July 2026 update, and allows non-admin users to modify registry hives of other accounts, posing a significant privilege escalation risk. Microsoft is investigating the vulnerability and committed to addressing it, while the incident highlights ongoing challenges in coordinated vulnerability disclosure and security patching.

https://thehackernews.com/2026/07/researcher-drops-new-windows-zero-day.html

Microsoft’s Secure Boot Has Been Broken for a Decade and No One Noticed Until Now

Researchers at security firm ESET discovered that Microsoft’s Secure Boot, designed to prevent malicious firmware infections, has been bypassable for 13 years due to old, vulnerable “shim” binaries that were never revoked despite known defects. This flaw affects both Windows and Linux devices by allowing attackers to load malicious firmware at boot time, persisting even after OS reinstallation; Microsoft only revoked the faulty shims after ESET’s report in June 2026. The incident highlights inherent complexity and trust issues in the Secure Boot model, which depends heavily on Microsoft’s oversight and has struggled to handle revocations and scaling effectively.

https://arstechnica.com/security/2026/07/microsoft-secure-boot-has-been-broken-for-most-of-its-existence/

Microsoft Patches Record 622 Flaws, Including Two Zero-Days Under Active Attack

Microsoft released its largest Patch Tuesday to date, addressing 622 vulnerabilities, including two zero-day elevation-of-privilege flaws actively exploited in SharePoint Server (CVE-2026-56164) and Active Directory Federation Services (CVE-2026-56155). Organizations are urged to prioritize these patches despite their moderate severity ratings, as both affect critical identity and collaboration infrastructure, and attackers are currently exploiting them. The update also ends support for SharePoint Server 2016 and 2019, and continues Kerberos RC4 hardening, which may cause authentication issues if service accounts still rely on RC4.

https://thehackernews.com/2026/07/microsoft-patches-record-622-flaws.html

Evolving Windows Vulnerability Management to Meet the Speed of AI-powered Discovery

Microsoft is enhancing Windows vulnerability management by leveraging AI-powered tools like the multi-model agentic scanning harness (MDASH) to accelerate discovery, prioritization, and remediation of security issues across its codebase. The company integrates AI into its engineering and validation processes to speed up fixes while maintaining update quality, and provides customers with tools and guidance to deploy timely security updates safely, supporting a shift toward continuous, risk-based patching to reduce exposure amid growing AI-driven vulnerability discovery.

https://blogs.windows.com/windowsexperience/2026/07/09/evolving-windows-vulnerability-management-to-meet-the-speed-of-ai-powered-discovery/

Patch for Windows Defender 0-Day Could Allow Attackers to Fill Hard Disk

A patch released by Microsoft to fix a zero-day vulnerability (CVE-2026-50656) in the Windows Defender malware protection engine may cause affected Windows machines to write excessively large files that can fill the hard disk. Researcher NightmareEclipse reported that new defense-in-depth mitigations introduced in the patch cause the engine to leak data when handling certain files and their associated Zone.Identifier metadata, potentially allowing attackers to exhaust disk space via specially crafted SMB server responses. Microsoft has not yet confirmed the disk-filling behavior, while the researcher’s ongoing public disclosures highlight a continued dispute with Microsoft over vulnerability handling.

https://arstechnica.com/security/2026/07/patch-for-windows-defender-0-day-could-allow-attackers-to-fill-hard-disk/

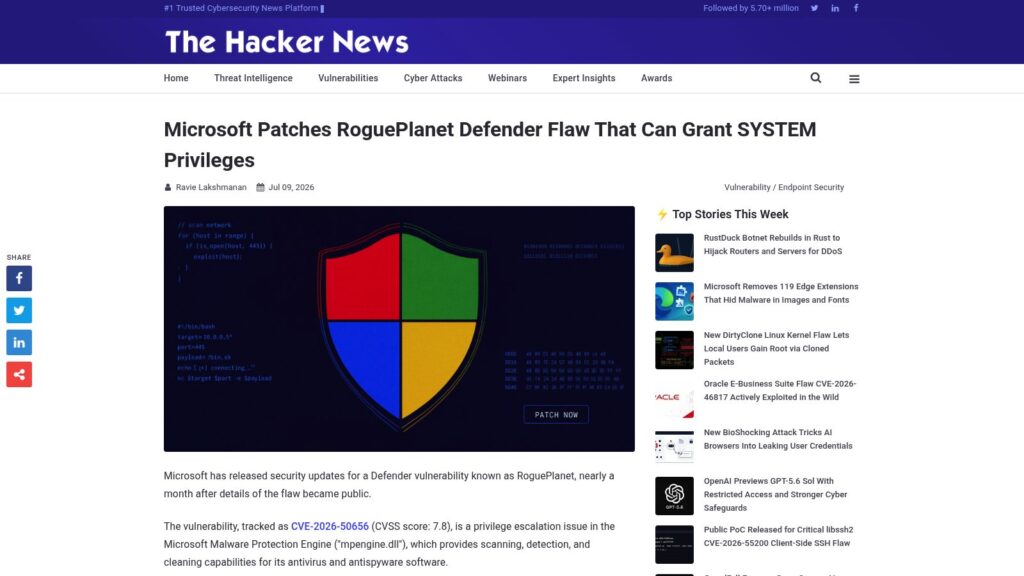
Microsoft Patches RoguePlanet Defender Flaw That Can Grant SYSTEM Privileges

Microsoft has released a security update to patch a privilege escalation vulnerability known as RoguePlanet (CVE-2026-50656) in its Malware Protection Engine, which could allow attackers to gain SYSTEM-level privileges and execute arbitrary code. The flaw, disclosed by researcher Chaotic Eclipse, exploited a race condition and affected fully patched Windows systems, but Microsoft’s update has mitigated the issue along with adding defense-in-depth improvements. Additionally, the researcher identified a potential new data leak caused by the patch that requires further investigation.

https://thehackernews.com/2026/07/microsoft-patches-rogueplanet-defender.html

Microsoft Confirms RoguePlanet Defender Zero-Day, Says Patch Is in Development

Microsoft has confirmed a privilege escalation zero-day vulnerability in Microsoft Defender, known as RoguePlanet (CVE-2026-50656), and is developing a patch to address it. The flaw, disclosed by researcher Chaotic Eclipse, exploits a race condition that can grant SYSTEM-level access regardless of Defender’s real-time protection setting.

https://thehackernews.com/2026/06/microsoft-confirms-rogueplanet-defender_02022423645.html

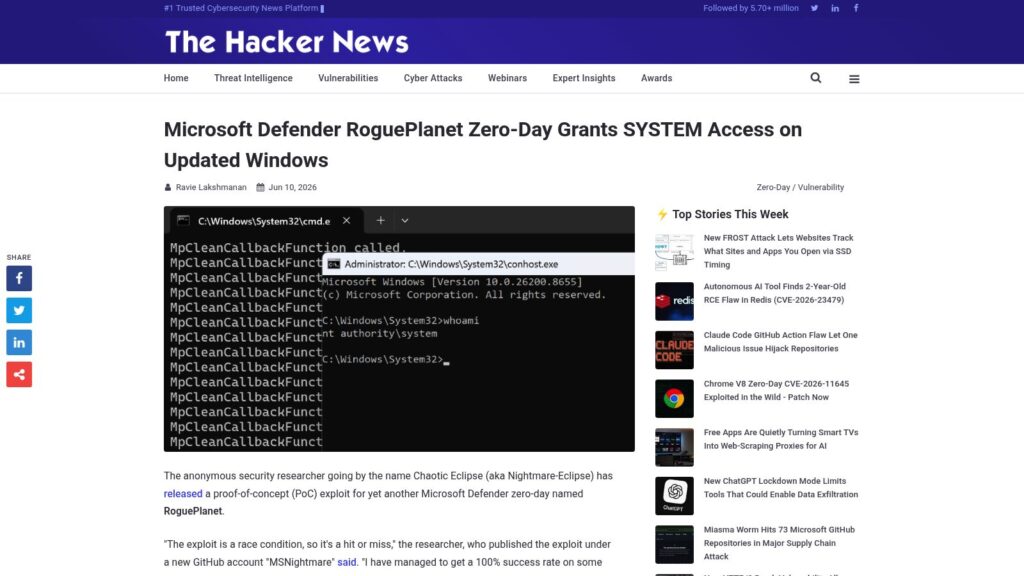
Microsoft Defender RoguePlanet Zero-Day Grants SYSTEM Access on Updated Windows

A security researcher known as Chaotic Eclipse has released a proof-of-concept exploit for a Microsoft Defender zero-day vulnerability called RoguePlanet, which enables privilege escalation to SYSTEM access on fully patched Windows 10 and 11 machines. The exploit, a race condition, allows attackers to run arbitrary code and remains effective despite recent updates, although it currently does not work on Windows Server without modification. This disclosure follows a series of public Microsoft Defender vulnerabilities revealed by the researcher amid a dispute with Microsoft over the handling of vulnerability reports and coordinated disclosure.

https://thehackernews.com/2026/06/microsoft-defender-rogueplanet-zero-day.html

Scroll to Top