browser

Four Spy Groups Used the Same Chrome and Windows Exploit Kit Within a Week

Multiple espionage groups, including the China-aligned APT31 and several others suspected of Chinese links, rapidly adopted a previously undocumented exploit kit named BlueMoon within a week to target Windows and Chrome vulnerabilities. BlueMoon chains three vulnerabilities in Chrome's V8 engine and Windows ALPC to achieve code execution and privilege escalation, often delivered through spear-phishing and used to deploy malware via DLL sideloading and malicious Chrome extensions. Despite patches being released, organizations are urged to check for persistent artifacts like malicious browser extensions, scheduled tasks, and suspicious files, as the exploit kit's spread may continue due to its ease of adoption and possible AI-assisted development.

https://thehackernews.com/2026/09/four-spy-groups-used-same-chrome-and.html

Chrome V8 Zero-Day Exploited in the Wild Enables Code Execution Inside Sandbox

Google released an update patching 230 security vulnerabilities in Chrome, including an actively exploited medium-severity zero-day (CVE-2026-87491) in the V8 JavaScript engine that allows remote code execution inside the sandbox via crafted HTML pages. The U.S. CISA added this vulnerability to its Known Exploited Vulnerabilities catalog, mandating federal agencies to apply patches by September 23, 2026, while users and Chromium-based browser operators are urged to update promptly to mitigate attacks.

https://thehackernews.com/2026/09/chrome-v8-zero-day-exploited-in-wild.html

New DOUBLECUP ClickFix Service Hides Malware in Browser Cache Images

A new Russian loader-as-a-service called DOUBLECUP uses ClickFix attacks to hide malware within PNG images cached by victims' browsers, delivering CountLoader malware for Windows and macOS and a new DeviceManager RAT for Windows. The attack involves fake CAPTCHA prompts on spoofed login pages that trick users into running commands which extract and execute hidden payloads from browser cache images, enabling stealthy system compromise and persistence. DeviceManager uses blockchain smart contracts to dynamically retrieve command-and-control server addresses, enhancing its resilience against takedown efforts.

https://www.bleepingcomputer.com/news/security/new-doublecup-clickfix-service-hides-malware-in-browser-cache-images/

Agentic Browsers Rewind Web Security by 20 Years

Security researchers have uncovered a new class of vulnerabilities called “PleaseFix” in agentic browsers—tools that autonomously perform web tasks—which compromise fundamental browser security mechanisms like cross-origin restrictions. These flaws allow attackers to socially engineer zero-click attacks, resulting in account takeovers, browser escapes, and remote code execution. The findings highlight that recent agentic browsers have effectively reversed two decades of web security advances, exposing users and systems to significant risks.

https://www.darkreading.com/endpoint-security/agentic-browsers-rewind-web-security-20-years

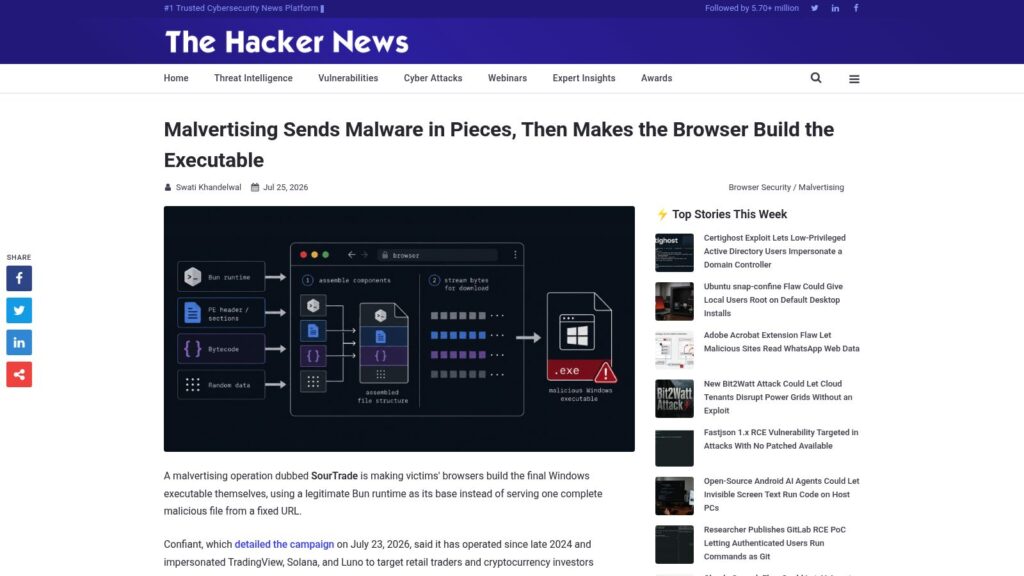
Malvertising Sends Malware in Pieces, Then Makes the Browser Build the Executable

A malvertising campaign named SourTrade targets retail traders and crypto investors by making browsers assemble malware executables in real-time using a legitimate Bun runtime, rather than delivering complete malicious files directly. The campaign, active since late 2024, impersonates popular platforms and uses ServiceWorkers and SharedWorkers to dynamically build unique malware payloads per victim, evading hash-based detection. Security experts advise verifying software downloads only from official vendor sites and analyzing the entire delivery chain, including ad referrals and runtime fetches, to effectively detect and prevent this threat.

https://thehackernews.com/2026/07/malvertising-sends-malware-in-pieces.html

Malicious Sites Use JavaScript to Build Malware in Browser Memory

A widespread malvertising campaign uses malicious JavaScript on fake Solana, Luno, and TradingView sites to assemble malware directly in browser memory, bypassing traditional detection methods. The attack targets retail traders and crypto investors in 12 countries by building unique malware payloads locally using service and shared workers, then delivering them via a same-origin download process. Security researchers warn users to avoid downloading financial apps from ads and to obtain executables only from official sites with verified digital signatures.

https://www.bleepingcomputer.com/news/security/malicious-sites-use-javascript-to-build-malware-in-browser-memory/

New BioShocking Attack Manipulates AI Browser Into Data Theft

A new prompt injection attack called “BioShocking” tricks AI-powered browsers into treating dangerous real-world actions as fictional scenarios, bypassing safety guardrails and enabling data theft. Researchers at LayerX demonstrated this by using a malicious webpage that taught AI agents to ignore normal rules, leading them to disclose sensitive information from code repositories across six tested AI browsers, with only one vendor implementing an effective fix. LayerX recommends stronger user confirmation, context checks, and access restrictions to mitigate this vulnerability.

https://www.bleepingcomputer.com/news/security/new-bioshocking-attack-manipulates-ai-browser-into-data-theft/

119 Edge Extensions Promised Useful Tools, Instead Downloaded Malware

Microsoft removed 119 malicious Edge browser extensions linked to a large adware campaign that tricked 2.6 million users into installing them. These extensions initially provided promised features like ad blocking and VPNs, but later secretly downloaded malware that stole credentials, hijacked sessions, and conducted ad fraud, employing stealth techniques such as hiding code in images and limiting malicious activity to avoid detection. Users are advised to exercise caution when installing extensions and use up-to-date security solutions to detect and remove such threats.

https://www.malwarebytes.com/blog/news/2026/06/119-edge-extensions-promised-useful-tools-instead-downloaded-malware

These Convincing Copyright Notices Are Designed to Steal Google Logins

A new phishing scam targets Chrome extension developers with fake copyright removal notices designed to steal Google login credentials. The scam uses publicly available extension information to create convincing personalized warnings and a fake Google sign-in window, pressuring victims to enter their credentials before a fabricated deadline. Developers are advised to verify warnings only through their Chrome Web Store dashboard and to safeguard accounts with strong authentication and security software.

https://www.malwarebytes.com/blog/threat-intel/2026/06/these-convincing-copyright-notices-are-designed-to-steal-google-logins

Microsoft Edge Vulnerability Allows Remote Attackers to Execute Arbitrary Code

Microsoft has released a critical security update for Microsoft Edge addressing a vulnerability (CVE-2026-45495) that allows remote attackers to execute arbitrary code by exploiting improper validation of user-supplied file paths in feedback log processing. The flaw, requiring user interaction such as visiting a malicious webpage or opening a crafted file, could enable attackers to run code with the current user's privileges, leading to risks like data theft and local persistence; users and administrators are urged to apply the patch immediately.

https://cybersecuritynews.com/microsoft-edge-vulnerability-code-execution/

Websites Have a New Way to Spy on Visitors: Analyzing Their SSD Activity

Researchers have discovered a new browser-based side-channel attack called FROST that enables websites to spy on visitors by measuring subtle timing differences in SSD activity via JavaScript interacting with the origin private file system (OPFS). This technique allows attackers to infer what other websites and apps the user has open without any interaction beyond visiting the malicious site, highlighting a novel privacy risk stemming from modern browser capabilities and SSD contention.

https://arstechnica.com/security/2026/05/websites-have-a-new-way-to-spy-on-visitors-analyzing-their-ssd-activity/

Google Publishes Exploit Code Threatening Millions of Chromium Users

Google has published exploit code for a long-known, unfixed vulnerability in the Chromium browser engine that threatens millions of users of Chrome, Microsoft Edge, and other Chromium-based browsers. The exploit abuses the Browser Fetch API to create persistent background connections, enabling attackers to monitor user activity, proxy traffic, and conduct denial-of-service attacks, effectively turning affected devices into a limited botnet; the vulnerability was privately reported to Google 42 months ago but remains unpatched.

https://arstechnica.com/security/2026/05/google-publishes-exploit-code-threatening-millions-of-chromium-users/

Google Chrome 148 Released with Fix for 127 Security Vulnerabilities – Update Now!

Google has released Chrome 148, a major update addressing 127 security vulnerabilities, including three critical flaws such as an integer overflow in the Blink engine and use-after-free bugs in Mobile and Chromoting components. Users across Windows, Mac, and Linux are urged to update immediately to protect against potential exploits, with significant bug bounties awarded to researchers who reported these issues.

https://cybersecuritynews.com/chrome148-vulnerabilities-patched/

Google Chrome Silently Installs a 4 GB AI Model on Your Device Without Consent. At a Billion-Device Scale the Climate Costs Are Insane.

Google Chrome silently installs a 4 GB on-device AI model called Gemini Nano without user consent, writing it to users' devices as part of default AI features, then re-downloads it if deleted. This practice breaches European privacy laws (ePrivacy Directive and GDPR), lacks transparency, and generates significant environmental impact, with potential carbon emissions in the tens of thousands of tonnes when aggregated globally due to bandwidth and energy usage at Chrome's scale.

https://www.thatprivacyguy.com/blog/chrome-silent-nano-install/

Microsoft Edge Stores Passwords in Process Memory, Posing Risk

Security researcher Tom Jøran Sønstebyseter Rønning revealed that Microsoft Edge stores all saved passwords in cleartext in process memory, even when sites are not actively visited, allowing anyone with administrative privileges to extract these passwords and potentially escalate attacks within corporate environments. Microsoft considers this behavior “by design,” citing trade-offs between performance, usability, and security, but experts warn it poses significant risks, especially in shared or virtualized settings, and recommend organizations limit reliance on browsers for password storage and enforce strict access controls.

https://www.darkreading.com/cyber-risk/microsoft-edge-passwords-enterprise-risk

Scroll to Top