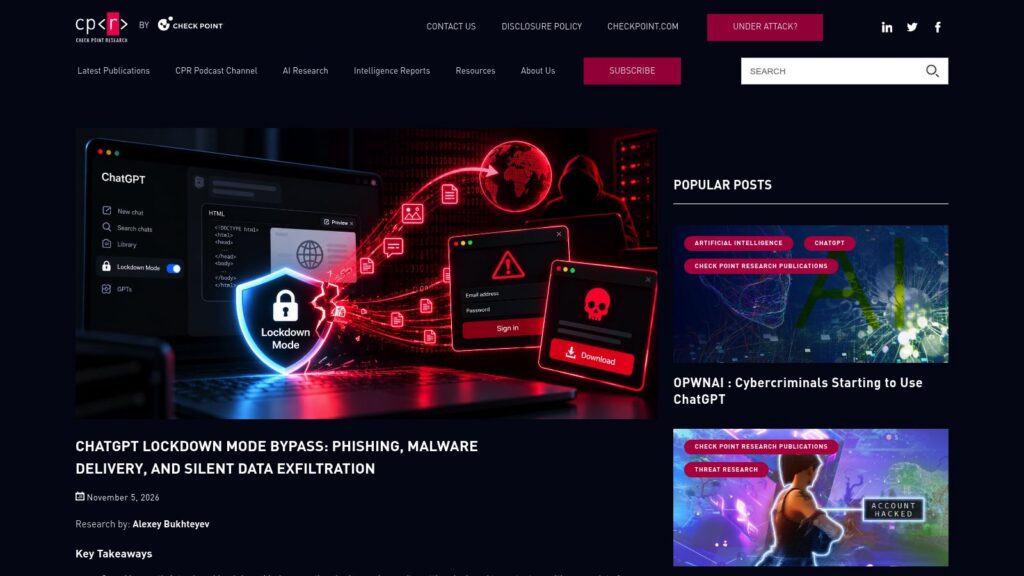
Check Point Research discovered a vulnerability in ChatGPT’s recently introduced Lockdown Mode that allowed attackers to bypass its core protections, enabling silent exfiltration of chat data, phishing via spoofed application windows, and malware delivery. The flaw exploited permissive sandbox iframe permissions to open pop-ups outside the sandbox, facilitating covert data theft and social engineering attacks, including zero-click exploitation in the ChatGPT Classic app. OpenAI fixed the issue by removing risky permissions from the HTML-preview sandbox iframe, closing the attack vector.
ChatGPT Lockdown Mode Bypass: Phishing, Malware Delivery, and Silent Data Exfiltration