
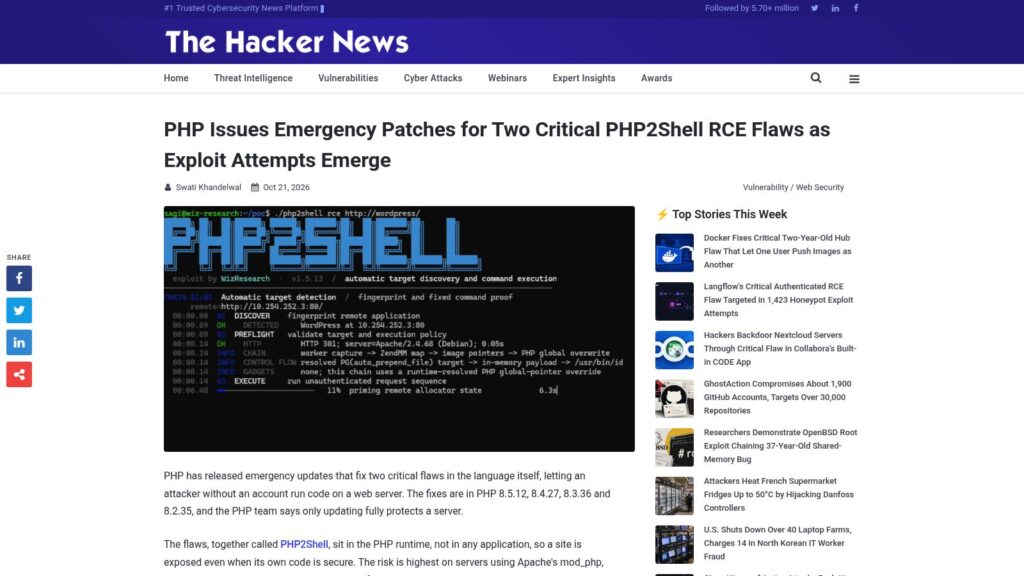
PHP has released emergency patches for two critical remote code execution vulnerabilities, collectively known as PHP2Shell, affecting nearly all versions from PHP 5.4 onward. These flaws, rated 9.2 CVSS, allow unauthenticated attackers to execute code on web servers at the runtime level, with the highest risk on Apache mod_php setups; active exploitation attempts have already been observed, prompting urgent updates to PHP versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35 to fully protect servers. The PHP Foundation acknowledged delayed fixes due to past challenges but emphasized that patching is the only reliable mitigation, as configuration workarounds do not fully prevent exploitation.
https://thehackernews.com/2026/10/php-issues-emergency-patches-for-two.html