
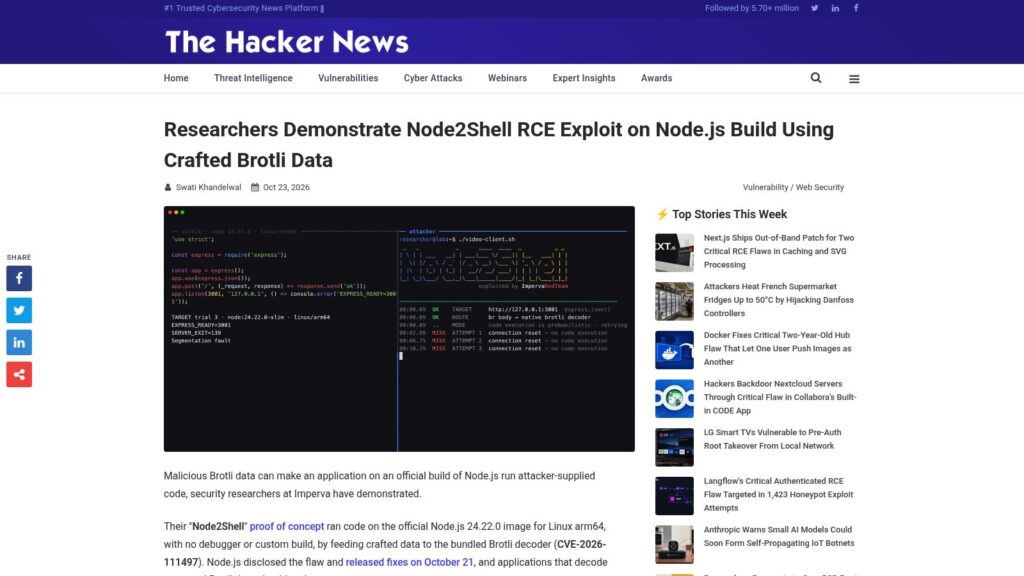
Security researchers at Imperva demonstrated a remote code execution exploit, dubbed “Node2Shell,” targeting an official Node.js 24.22.0 build by using crafted malicious Brotli data to trigger a vulnerability in the bundled Brotli decoder (CVE-2026-111497). The flaw affects Node.js versions 22.x, 24.x, and 26.x lines, allowing attackers to execute arbitrary code via Brotli-compressed HTTP request or response bodies, and has been fixed in Node.js 24.22.1 by adopting an upstream Brotli patch that rejects malformed streams. Users and service providers are urged to update to patched Node.js releases and limit untrusted Brotli traffic, as no workaround exists within Node.js itself.
https://thehackernews.com/2026/10/researchers-demonstrate-node2shell-rce.html