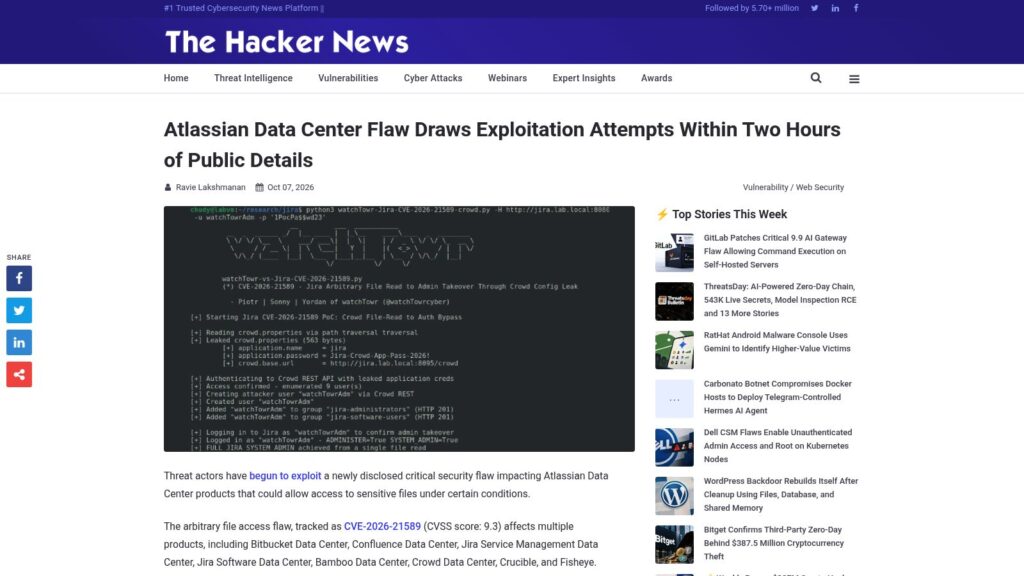
A critical arbitrary file access vulnerability (CVE-2026-21589) affecting multiple Atlassian Data Center products has been actively exploited within two hours of its public disclosure, allowing unauthenticated attackers to access sensitive files if the exact file path is known. Atlassian has released patches and recommends immediate mitigation steps, while telemetry shows exploitation attempts originating from IP addresses in Japan and the U.S., raising urgent patching priorities for affected organizations.
https://thehackernews.com/2026/10/atlassian-data-center-flaw-draws.html