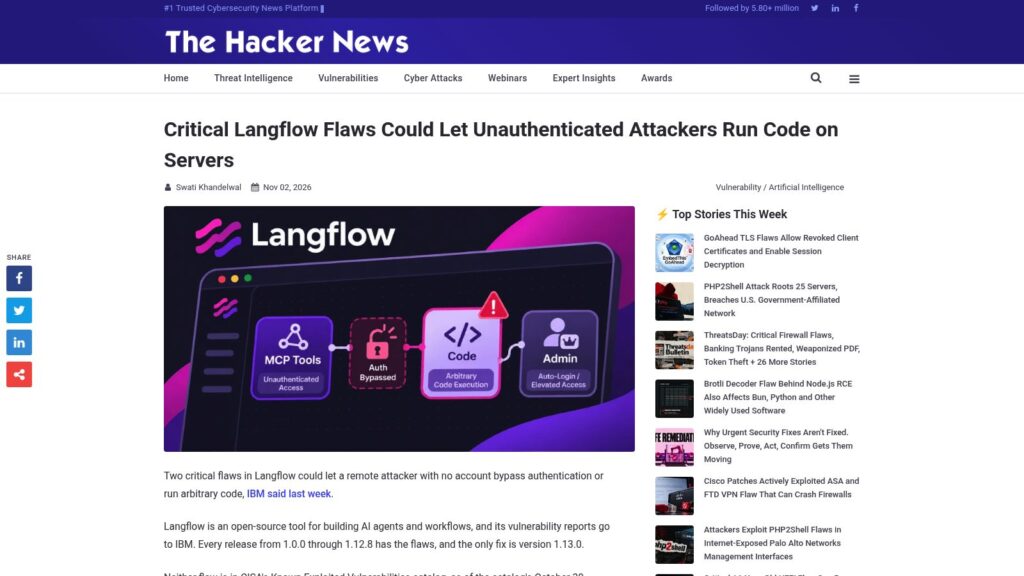
Two critical vulnerabilities in Langflow, an open-source AI workflow tool, allow unauthenticated attackers to bypass authentication and execute arbitrary code on servers, IBM reported. These flaws affect all Langflow versions from 1.0.0 through 1.12.8, with the security issues resolved only in version 1.13.0, which disables insecure auto-login by default; administrators are urged to upgrade promptly to mitigate the risks.
https://thehackernews.com/2026/11/critical-langflow-flaws-could-let.html