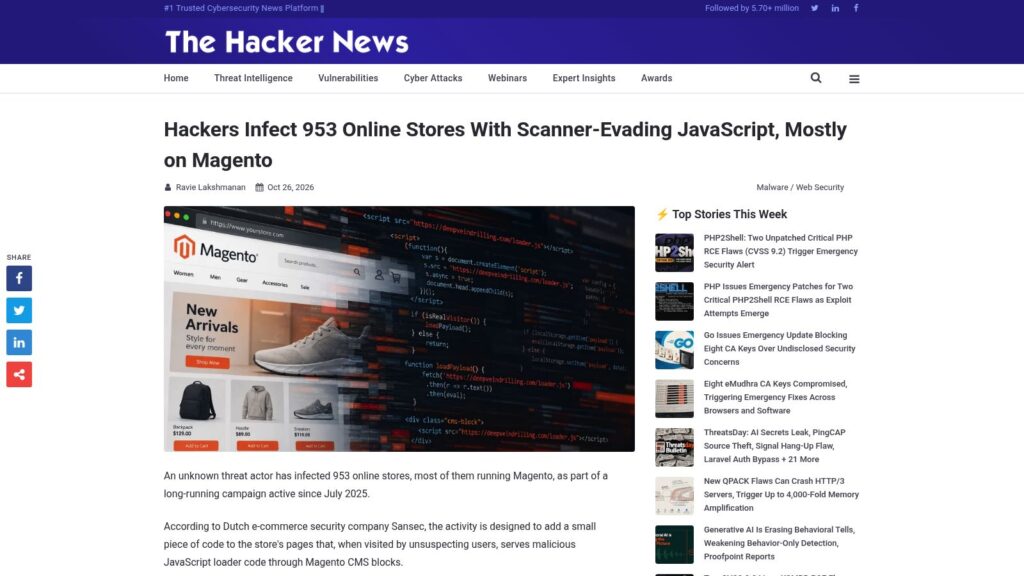
A long-running hacking campaign since July 2025 has infected 953 online stores, predominantly running Magento, by injecting scanner-evading malicious JavaScript into CMS blocks to target real shoppers while avoiding detection by security tools. The attackers exploited vulnerabilities such as PolyShell (CVE-2026-48356) and SessionReaper (CVE-2025-54236) to gain access, and use multiple rotating domains to host loader scripts that include bot filtering and persistent payload storage. Site owners are urged to audit for suspicious CMS blocks and administrator accounts, apply security patches, and enforce strong passwords to mitigate the threat.
https://thehackernews.com/2026/10/hackers-infect-953-online-stores-with.html