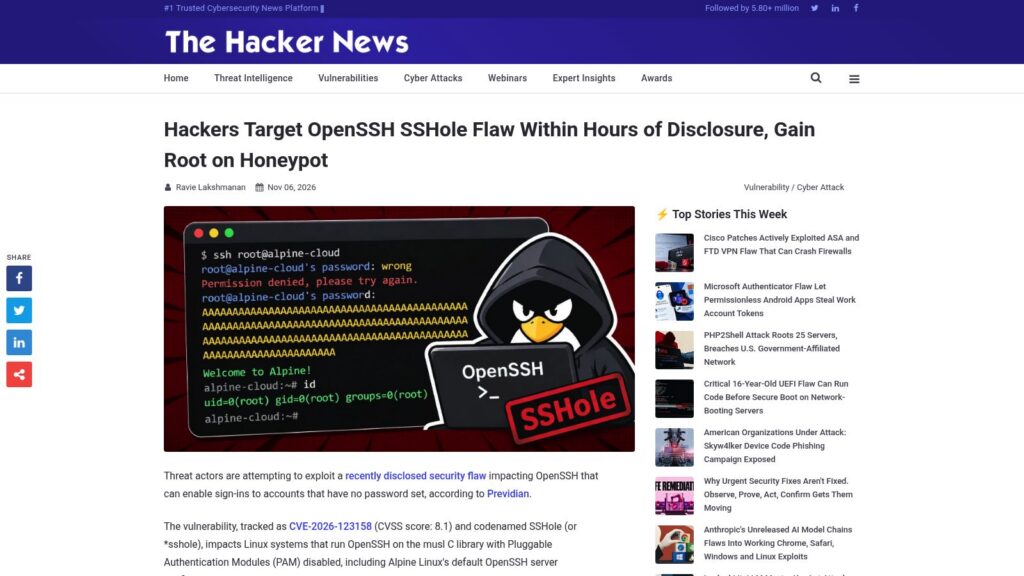
Hackers began exploiting a recently disclosed high-severity OpenSSH vulnerability (CVE-2026-123158, “SSHole”) within hours of its publication, targeting Linux systems running OpenSSH on musl libc with PAM disabled, such as Alpine Linux. The flaw allows unauthenticated attackers to bypass password authentication on accounts configured without passwords by sending oversized passwords, granting access with the compromised account’s existing privileges, including root access, as confirmed by successful exploitation on a honeypot. Users are urged to update to OpenSSH 10.6p2 and review login logs for unusual password acceptance on accounts meant to be passwordless.
https://thehackernews.com/2026/11/hackers-exploited-openssh-sshole-flaw.html