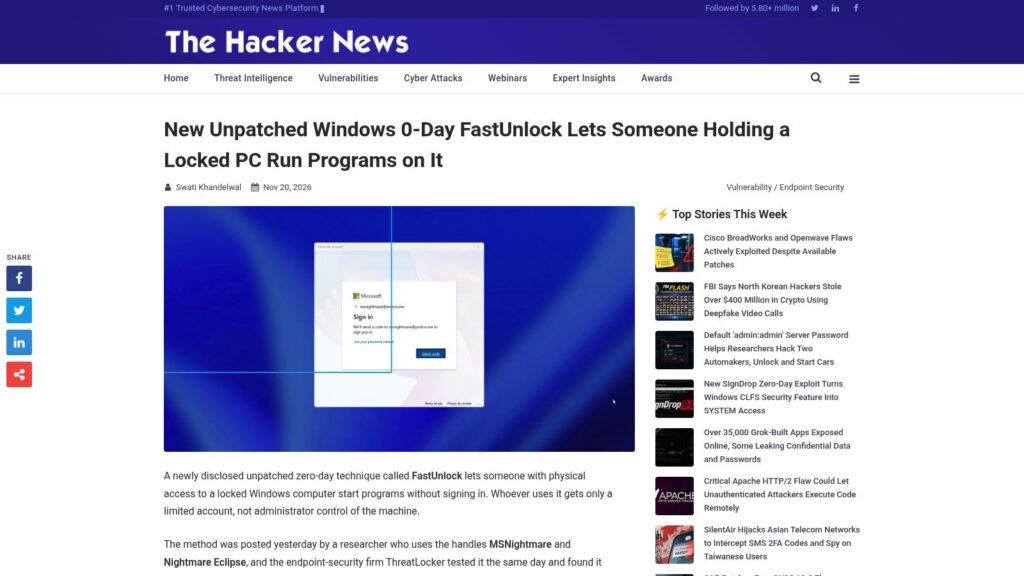
A newly disclosed unpatched Windows zero-day vulnerability called FastUnlock allows an attacker with physical access to a locked PC to launch programs without signing in, though only with limited user privileges. The exploit leverages the Windows Narrator screen reader and accessible Microsoft account recovery options at the lock screen, bypassing the screen lock without breaking disk encryption. With no patch available yet, users are advised to secure physical access, enable BitLocker startup PINs, and fully shut down or hibernate devices to mitigate this attack risk.
https://thehackernews.com/2026/11/new-unpatched-windows-0-day-fastunlock.html