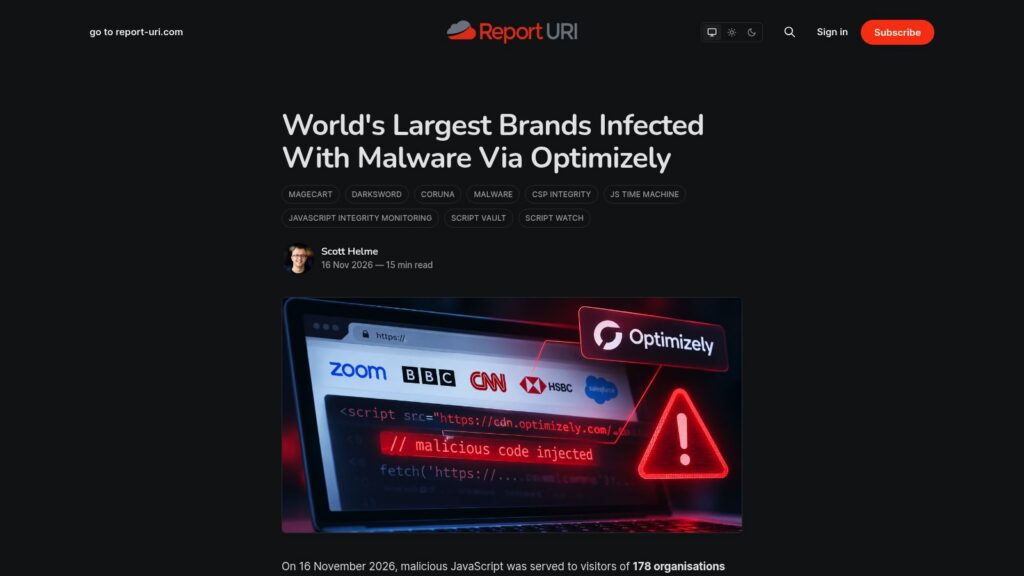
On November 16, 2026, attackers compromised the Optimizely Web experimentation platform to inject malicious JavaScript into the snippets of 178 major organizations—including Zoom, BBC, CNN, Salesforce, and HSBC—serving malware that swapped cryptocurrency wallet addresses, skimmed payment cards, stole cookies and screenshots, and deployed iOS exploit kits Coruna and DarkSword. The malware was delivered via the trusted Optimizely CDN by unauthorized changes to customer “Project JavaScript” fields, highlighting the risk that third-party dependencies can become attack vectors without breaching the organizations’ own infrastructure. While most infected snippets have been cleaned, the incident underscores the importance of stringent Content Security Policies and continuous monitoring of third-party scripts to detect and prevent such supply-chain malware attacks.
https://blog.report-uri.com/worlds-largest-brands-infected-with-malware-via-optimizely/