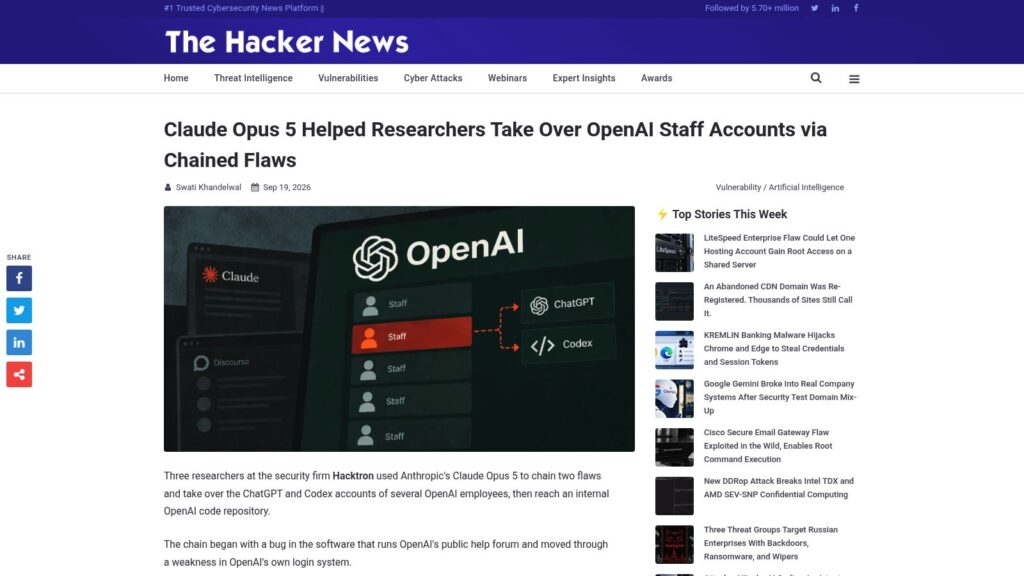
Researchers at Hacktron leveraged Anthropic’s Claude Opus 5 to chain vulnerabilities—starting from a memory-corrupting image flaw in OpenAI’s public forum software to weaknesses in OpenAI’s single sign-on system—enabling them to take over OpenAI staff ChatGPT and Codex accounts and gain access to internal code repositories. The team reported the issues responsibly, leading to a fix within 14 hours and a $6,500 bounty, while highlighting broader risks where shared single sign-on between public and internal systems can escalate compromises. They also demonstrated AI-assisted exploit development, underscoring how advanced models are accelerating offensive security research and attack capabilities.
https://thehackernews.com/2026/09/claude-opus-5-helped-researchers-take.html