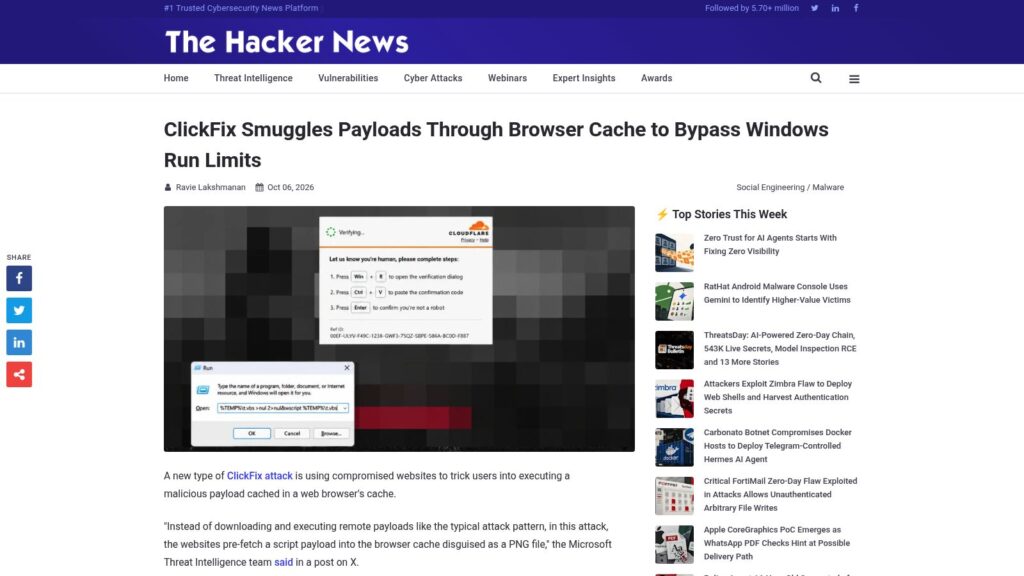
A new ClickFix attack technique abuses compromised websites to prefetch malicious script payloads disguised as images into browser caches, bypassing Windows Run command character limits by executing cached content locally. The attack chain uses VBScript and PowerShell to download and execute further malware stages in memory, enabling credential theft and persistent access while evading traditional detection methods. Microsoft advises enhanced monitoring of browser cache activity and warns users against running commands prompted by CAPTCHA or error messages to mitigate this social engineering threat.
https://thehackernews.com/2026/10/clickfix-smuggles-payloads-through.html