Dirty Frag Linux Vulnerability Let Attackers Gain Root Privileges – PoC Released
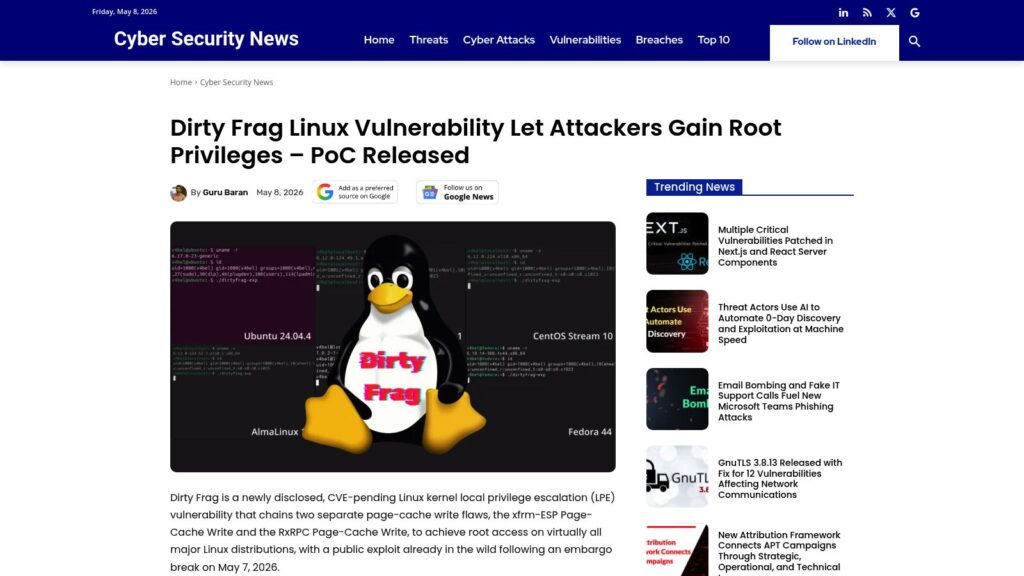
Dirty Frag is a newly disclosed Linux kernel local privilege escalation vulnerability that chains two separate page-cache write flaws, allowing attackers to gain root privileges on virtually all major Linux distributions. Discovered by security researcher Hyunwoo Kim, the exploit modifies page cache in RAM deterministically without requiring timing windows or crashing the kernel, with a public proof-of-concept released following an embargo breach on May 7, 2026. Immediate mitigation involves disabling affected kernel modules until distribution-level patches, which are partially merged upstream, become available.

https://cybersecuritynews.com/dirty-frag-linux-vulnerability/
Critical Ollama Memory Leak Vulnerability Exposes 300,000 Servers Globally

A critical memory leak vulnerability named “Bleeding Llama” affects Ollama, a popular platform for running local AI models, exposing approximately 300,000 internet-facing servers globally. This flaw allows unauthenticated attackers to extract sensitive data directly from server memory by exploiting a weakness in processing uploaded model files, potentially leaking prompts, environment variables, and confidential information; users are urged to update to version 0.17.1 and secure exposed deployments immediately.

https://cybersecuritynews.com/ollama-vulnerability-exposes-servers/

Google Chrome 148 Released with Fix for 127 Security Vulnerabilities – Update Now!

Google has released Chrome 148, a major update addressing 127 security vulnerabilities, including three critical flaws such as an integer overflow in the Blink engine and use-after-free bugs in Mobile and Chromoting components. Users across Windows, Mac, and Linux are urged to update immediately to protect against potential exploits, with significant bug bounties awarded to researchers who reported these issues.

https://cybersecuritynews.com/chrome148-vulnerabilities-patched/

Google Chrome Silently Installs a 4 GB AI Model on Your Device Without Consent. At a Billion-Device Scale the Climate Costs Are Insane.

Google Chrome silently installs a 4 GB on-device AI model called Gemini Nano without user consent, writing it to users’ devices as part of default AI features, then re-downloads it if deleted. This practice breaches European privacy laws (ePrivacy Directive and GDPR), lacks transparency, and generates significant environmental impact, with potential carbon emissions in the tens of thousands of tonnes when aggregated globally due to bandwidth and energy usage at Chrome’s scale.

https://www.thatprivacyguy.com/blog/chrome-silent-nano-install/

Microsoft Edge Stores Passwords in Process Memory, Posing Risk

Security researcher Tom Jøran Sønstebyseter Rønning revealed that Microsoft Edge stores all saved passwords in cleartext in process memory, even when sites are not actively visited, allowing anyone with administrative privileges to extract these passwords and potentially escalate attacks within corporate environments. Microsoft considers this behavior “by design,” citing trade-offs between performance, usability, and security, but experts warn it poses significant risks, especially in shared or virtualized settings, and recommend organizations limit reliance on browsers for password storage and enforce strict access controls.

https://www.darkreading.com/cyber-risk/microsoft-edge-passwords-enterprise-risk

Critical Apache HTTP/2 Flaw (CVE-2026-23918) Enables DoS and Potential RCE

The Apache Software Foundation has released updates to fix a critical vulnerability (CVE-2026-23918) in Apache HTTP Server 2.4.66 that allows denial-of-service (DoS) attacks and potential remote code execution (RCE) via a double-free bug in HTTP/2 protocol handling. The flaw can be exploited by sending specific HTTP/2 frames, with the RCE path particularly feasible on systems using the default Apache Portable Runtime mmap allocator, leading to high risk for widely deployed servers.

https://thehackernews.com/2026/05/critical-apache-http2-flaw-cve-2026.html

Some Ubuntu Services Are Still Down Following Outages After DDoS Attack

Some Ubuntu services experienced outages for nearly a full day following a sustained Distributed Denial of Service (DDoS) attack that disrupted installs, updates, and Canonical’s web infrastructure. The attack was claimed by an Iraqi hacktivist group called The Islamic Cyber Resistance in Iraq 313 Team, which reportedly used a booter service named Beamed to launch the attack.

https://www.techradar.com/pro/security/some-ubuntu-services-are-still-down-following-outages-after-ddos-attack

Critical Apache HTTP Server Flaw Exposes Millions of Servers to RCE Attacks

The Apache Software Foundation released version 2.4.67 of Apache HTTP Server to patch five vulnerabilities, including a critical double-free flaw (CVE-2026-23918) in version 2.4.66 that enables remote code execution via HTTP/2. Users are strongly urged to upgrade immediately to mitigate this high-severity risk affecting millions of servers worldwide.

https://cybersecuritynews.com/apache-http-server-rce/

cPanelSniper – PoC Exploit Disclosed for cPanel Vulnerability, 44,000 Servers Compromised

A critical authentication bypass vulnerability (CVE-2026-41940) in cPanel & WHM, exploited by a publicly released proof-of-concept tool named “cPanelSniper,” has compromised approximately 44,000 servers worldwide since at least February 2026. The flaw allows attackers to forge root sessions without valid credentials by injecting malicious session data, prompting emergency patches from cPanel, while security experts urge immediate updates and audits to prevent further exploitation.

https://cybersecuritynews.com/cpanelsniper-poc-exploit/

The Most Severe Linux Threat to Surface in Years Catches the World Flat-Footed

A critical local privilege escalation vulnerability in the Linux kernel, named CopyFail (CVE-2026-31431), has been publicly disclosed with exploit code that easily grants root access across virtually all Linux distributions. The flaw affects multi-tenant servers, Kubernetes containers, and CI/CD workflows, posing a severe threat as attackers can escalate privileges quickly on vulnerable systems before widespread patches are applied. Security experts warn this is one of the most serious Linux vulnerabilities in years, urging immediate investigation and mitigation by Linux users and vendors.

https://arstechnica.com/security/2026/04/as-the-most-severe-linux-threat-in-years-surfaces-the-world-scrambles/

I Left Port 22 Open on the Internet for 54 Days. Here’s Who Showed Up.

In a 54-day experiment, a honeypot mimicking an Ubuntu SSH server was left open on port 22, recording over 269,000 connection attempts from 7,556 unique IPs. The study revealed a constant flood of mostly automated attacks scanning for weak passwords, with a small fraction of sophisticated attackers deploying advanced techniques, including targeted crypto node intrusions; the findings underscore the relentless and noisy nature of internet scanning and the importance of robust SSH security practices.

https://arman-bd.hashnode.dev/i-left-port-22-open-on-the-internet-for-54-days-here-s-who-showed-up

cPanel 0-Day Authentication Bypass Vulnerability Actively Exploited in the Wild

A critical authentication bypass vulnerability (CVE-2026-41940) in cPanel & WHM has been actively exploited in the wild, allowing unauthenticated attackers to gain root-level access to hosting control panels. With a public proof-of-concept exploit released, cPanel has issued emergency patches and urged administrators to update immediately to prevent widespread compromise across millions of hosting accounts globally.

https://cybersecuritynews.com/cpanel-0-day-authentication-bypass-vulnerability/

Linux Kernel 0-Day “Copy Fail” Roots Every Major Distribution Since 2017

A critical zero-day vulnerability named “Copy Fail” (CVE-2026-31431) in the Linux kernel, affecting every major distribution since 2017, allows any unprivileged local user to gain root access by exploiting a flaw in the kernel’s cryptographic template via the AF_ALG socket and splice() system call. The vulnerability, discovered by Theori and exploited by Xint Code Research Team, enables file page cache corruption undetectable by integrity tools, and also facilitates Kubernetes container escapes; a patch has been released and administrators are urged to update immediately.

https://cybersecuritynews.com/linux-kernel-0-day-copy-fail/

Wiz Hands GitHub AI-aided Bug Report That Isn’t Total Slop

Wiz researchers discovered a high-severity vulnerability (CVE-2026-3854) in GitHub’s git infrastructure that allowed remote attackers full read/write access to private repositories using a single command. By leveraging AI-augmented tools for automated reverse engineering, they rapidly identified the flaw, leading to GitHub issuing fixes within six hours and awarding Wiz one of the largest payouts in its bug bounty history.

https://www.theregister.com/2026/04/29/github_woah_a_genuinely_helpful/

Critical Chrome Vulnerabilities Enables Remote Code Execution Attacks

Google has released a critical update for Chrome version 147.0.7727.137/138 that fixes 30 security vulnerabilities, including four severe use-after-free flaws enabling remote code execution attacks. Users and enterprises are strongly urged to update their browsers immediately to protect against remote attacks that could bypass Chrome’s sandbox and compromise systems without additional user interaction.

https://cybersecuritynews.com/chrome-vulnerabilities-2/

Scroll to Top