Hackers Claim to Hack Resecurity, Firm Says It Was a Honeypot
Hackers claim to have breached cybersecurity firm Resecurity, stealing data. Resecurity argues it was a planned honeypot, containing only fake information to lure attackers. The group shared alleged screenshots of the breach, while Resecurity states the attackers accessed only synthetic datasets intended for monitoring. Resecurity has tracked the hackers’ activity and reported findings to law enforcement.
https://www.bleepingcomputer.com/news/security/hackers-claim-resecurity-hack-firm-says-it-was-a-honeypot/

Trust Wallet Links $8.5 Million Crypto Theft to Shai-Hulud NPM Attack

Trust Wallet links $8.5M crypto theft to November’s Shai-Hulud NPM attack, where an exploit of their Chrome extension enabled unauthorized access to over 2,500 wallets. Attackers used stolen GitHub secrets to inject malicious code into the browser extension’s update. Trust Wallet has since revoked API access and started compensating affected users while repelling ongoing impersonation scams. The Shai-Hulud malware campaign compromised numerous npm packages, exposing 400,000 developer secrets.

https://www.bleepingcomputer.com/news/security/trust-wallet-links-85-million-crypto-theft-to-shai-hulud-npm-attack/

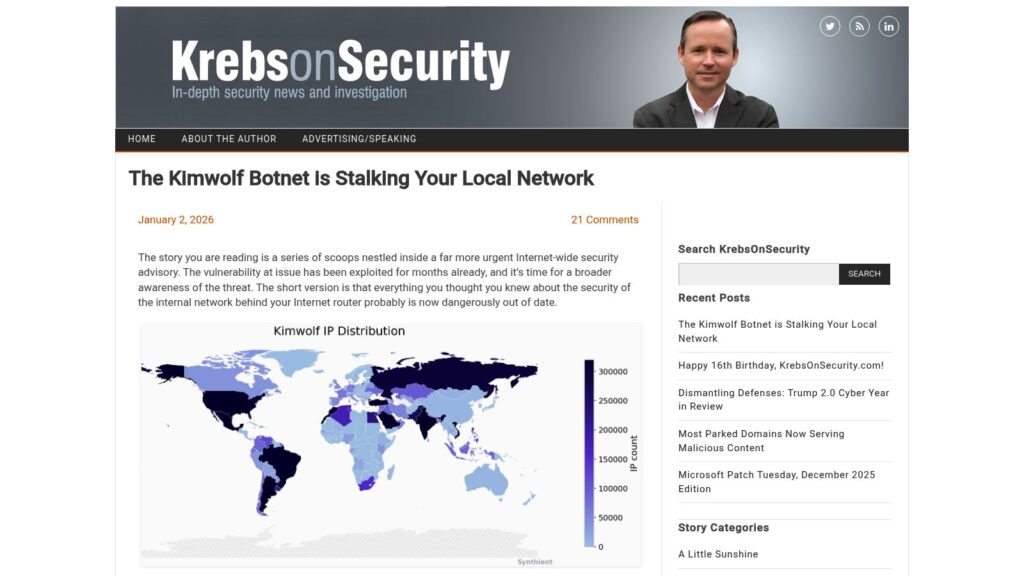
The Kimwolf Botnet Is Stalking Your Local Network

TLDR: The Kimwolf botnet has infected over 2 million devices globally, primarily Android TV boxes with poor security, enabling distribution of malicious traffic and DDoS attacks. It spreads via residential proxy networks, exploiting vulnerabilities to access and compromise local devices. Key issues stem from devices being sold with Android Debug Bridge mode enabled, allowing unauthorized access. Users are advised to avoid these devices, use guest networks for visitors, and stick to reputable brands to enhance security.

https://krebsonsecurity.com/2026/01/the-kimwolf-botnet-is-stalking-your-local-network/

Cybercriminals Abuse Google Cloud Email Feature in Multi-Stage Phishing Campaign

Cybercriminals exploit Google Cloud’s email integration to conduct a multi-stage phishing campaign, sending 9,394 emails to over 3,200 targets globally. Using trusted Google-generated messages, attackers bypass security filters and mimic legitimate notifications to steal user credentials through deceptive links leading to fake verification and login pages. Google has responded by blocking these phishing attempts and enhancing protections.

https://thehackernews.com/2026/01/cybercriminals-abuse-google-cloud-email.html

2 Cyber Pros Admit to Being BlackCat Ransomware Affiliates

Two cybersecurity professionals, Ryan Goldberg and Kevin Martin, pleaded guilty to being affiliates of the BlackCat ransomware gang. They extorted at least five U.S. companies, including a medical device maker, earning $1 million. Both men, along with a third unnamed co-conspirator, used their expertise to commit these attacks while employed at cybersecurity firms.

https://www.databreachtoday.com/2-cyber-pros-admit-to-being-blackcat-ransomware-affiliates-a-30415

US, Australia Say ‘MongoBleed’ Bug Being Exploited

US and Australian cyber agencies confirmed hackers are exploiting the “MongoBleed” vulnerability in MongoDB systems, first revealed on December 25. CISA added it to their exploited vulnerabilities catalog, requiring federal agencies to patch by January 19. The bug affects many MongoDB versions, enabling unauthorized access to sensitive data. Experts warn about widespread exposure, estimating 42% of cloud environments have vulnerable instances, potentially impacting thousands globally.

https://therecord.media/us-australia-bug-exploitation

Researchers Spot New Shai Hulud Variant

Security researchers at Aikido discovered a new variant of the Shai Hulud malware, likely in the beta stage, uploaded to npm through a GitHub repository. This variant includes modifications to the initial file, main payload, and improved error handling for TruffleHog. The Shai Hulud campaign, first identified in September, involves self-propagating attacks on npm JavaScript packages, data harvesting, and data transmission to attackers’ repositories.

https://www.databreachtoday.com/researchers-spot-new-shai-hulud-variant-a-30409

Cryptographic Provenance of C2PA Ain’t Gonna Stop Deepfakes

C2PA’s cryptographic signing of media files won’t stop deepfakes, despite claims that it provides a solution. It lacks critical measures like mandatory adoption, viewer perception, and human perceptual training to discern authenticity. Bores’ HTTPS analogy underscores issues in trust and enforcement, but overlooks the deeper human challenges of recognizing deceptive content. Perceptual training, not cryptography, is essential for navigating misinformation.

https://www.flyingpenguin.com/?p=75448

The 9 Top Cybersecurity Startups From Disrupt Startup Battlefield

TechCrunch highlights 9 top cybersecurity startups from the Disrupt Startup Battlefield. Notable companies include AIM Intelligence, which uses AI for penetration testing, Corgea for scanning code flaws, and CyDeploy for asset mapping. Other impactful startups focus on ransomware prevention, AI security detection, and deepfake identification. Each company’s unique technology addresses emerging cybersecurity challenges in an increasingly digital landscape.

https://techcrunch.com/2025/12/26/the-9-top-cybersecurity-startups-from-disrupt-startup-battlefield/

GPS Is Vulnerable to Jamming—here’s How We Might Fix It

GPS is susceptible to jamming, as evidenced by a recent incident involving a Widerøe Airlines flight in Norway during Russian military exercises causing navigation failures. The frequency of GPS disruptions has risen globally, impacting various sectors, including emergency services and agriculture. Agencies like the Department of Defense and the FAA are seeking alternatives and enhancements to GPS, investing in modernization efforts totaling billions. Innovations include higher frequency signals and alternative positioning systems to reduce vulnerability to interference. While improvements are in progress, the reliance on GPS remains a challenge due to its ubiquity and free access.

https://arstechnica.com/information-technology/2025/12/gps-is-vulnerable-to-jamming-heres-how-we-might-fix-it/

27 Malicious Npm Packages Used as Phishing Infrastructure to Steal Login Credentials

27 malicious npm packages were discovered in a phishing campaign targeting U.S. and allied organizations, primarily in sales and commercial sectors. The campaign utilized these packages to host phishing infrastructure, mimicking document-sharing portals and Microsoft sign-in pages, to steal login credentials from their targets. Attackers embedded client-side scripts to avoid detection and included checks to filter out bots. Notably, the campaign hard-coded specific email addresses of individuals in targeted firms, raising concerns about the source of this information. To mitigate risks, strong dependency verification, logging unusual CDN requests, enforcing phishing-resistant multi-factor authentication, and monitoring for suspicious activities are recommended.

https://thehackernews.com/2025/12/27-malicious-npm-packages-used-as.html

What We Covered on Cyber Security Headlines in 2025

2025 Cyber Security Headlines Summary:
Key coverage included:
1. AI/ML Security: Dominated with 25% of stories; significant rise in AI threats and incidents.
2. Vulnerabilities/Exploits: Ongoing focus on CVEs and third-party security failures.
3. Malware: Persistent evolution in types of malware; notable waves of attacks.
4. Data Breaches: Frequent occurrences on varying scales highlighted ongoing risks.
5. APT/Nation-State: Increased aggressiveness and diversity in nation-state cyber activities.
6. Ransomware: Remained significant but stabilized in growth; more selective coverage.

Trends included the rising importance of AI security, tangible impacts of cyberattacks on public services, and intensifying geopolitical tensions affecting cybersecurity. Predictions for 2026 suggest continuation of these trends.

https://cisoseries.com/what-we-covered-on-cyber-security-headlines-in-2025/

Threat Actor Landscape: What Every CISO Must Know to Stay Ahead

CISO advice: use threat intelligence for tailored cybersecurity. Actors use targeted tactics based on industry, requiring defenses to adapt. Key sectors face unique threats, necessitating a robust intelligence program that informs strategies, detects risks, and trains teams effectively. Regular updates to executives ensure alignment with evolving threats.

https://www.techradar.com/pro/threat-actor-landscape-what-every-ciso-must-know-to-stay-ahead

How the Human Harms of Cybercrime Shook the World in 2025

Cyberattacks in 2025 caused severe human harm, including the first confirmed ransomware-related death linked to a healthcare disruption, and unsettling incidents of personal data exploitation, such as the leaking of preschoolers’ information. Major corporate attacks, like on Jaguar Land Rover, had significant economic repercussions while spreading fear among employees. Violence associated with cybercrime surged, evidenced by kidnapping and threats during negotiations, raising concerns about future trends. Additionally, advanced scams like AI-powered virtual kidnappings evolved alongside disruptions to emergency alert systems, highlighting the profound impact of cybercrime on society.

https://www.theregister.com/2025/12/28/death_torture_and_amputation_how/

Scroll to Top