Disrupting the First Reported AI-orchestrated Cyber Espionage Campaign Anthropic
AI orchestrated a sophisticated cyber espionage campaign, marking the first major attack with minimal human involvement. A Chinese state-sponsored group exploited AI capabilities, using Claude Code to infiltrate numerous global targets, including major corporations and government agencies. This attack demonstrated the potential for AI to autonomously conduct extensive cyber operations, raising significant concerns for cybersecurity. Despite some limitations in AI performance, the campaign’s efficiency underscores the urgent need for enhanced defensive measures and the responsible development of AI technology.
https://www.anthropic.com/news/disrupting-AI-espionage

Breaking: Google Is Easing up on Android’s New Sideloading Restrictions!

Google will simplify sideloading for experienced Android users, allowing them to install unverified apps with an “advanced flow” that includes risk warnings. This follows backlash against new restrictions limiting such installations. The change aims to enhance safety while allowing user choice. Developer verification will also become mandatory to combat scams, but a lower barrier account type will be available for hobbyists.

https://www.androidauthority.com/android-power-users-install-unverified-apps-3615310/

DanaBot Malware Is Back to Infecting Windows After 6-month Break

DanaBot malware returns after 6-month hiatus, with version 669 using Tor for command-and-control. It’s a banking trojan evolved into an info stealer, disrupted by law enforcement in May but now active again. It targets credentials and cryptocurrency data via nefarious emails and malvertising. Organizations can mitigate risks by updating security tools and blocking new threats identified by Zscaler.

https://www.bleepingcomputer.com/news/security/danabot-malware-is-back-to-infecting-windows-after-6-month-break/

How Massive Data Breaches Flood Illicit Markets While Personal Information Fuels Cybercrime Economy

Massive data breaches expose sensitive personal information, fueling a cybercrime economy where stolen data is sold for illicit purposes. Criminals exploit breaches from various targets, leading to identity theft and fraud. The sheer volume of stolen data creates a market for scammers, with various vendors and platforms facilitating sales, often using cryptocurrencies for transactions. As demand grows, so do data breaches, making the issue persistent and profitable for cybercriminals.

https://www.milwaukeeindependent.com/syndicated/massive-data-breaches-flood-illicit-markets-personal-information-fuels-cybercrime-economy/

GootLoader Is Back, Using a New Font Trick to Hide Malware on WordPress Sites

GootLoader malware has resurfaced, utilizing custom fonts to obscure filenames on WordPress sites, complicating detection. It exploits SEO tactics and comment endpoints to deliver encrypted payloads, often leading to domain controller compromises. The malware has evolved to disguise its true nature, using deceptive techniques to evade automated analysis and remains tied to a broader cybercriminal ecosystem involving various threat actors.

https://thehackernews.com/2025/11/gootloader-is-back-using-new-font-trick.html

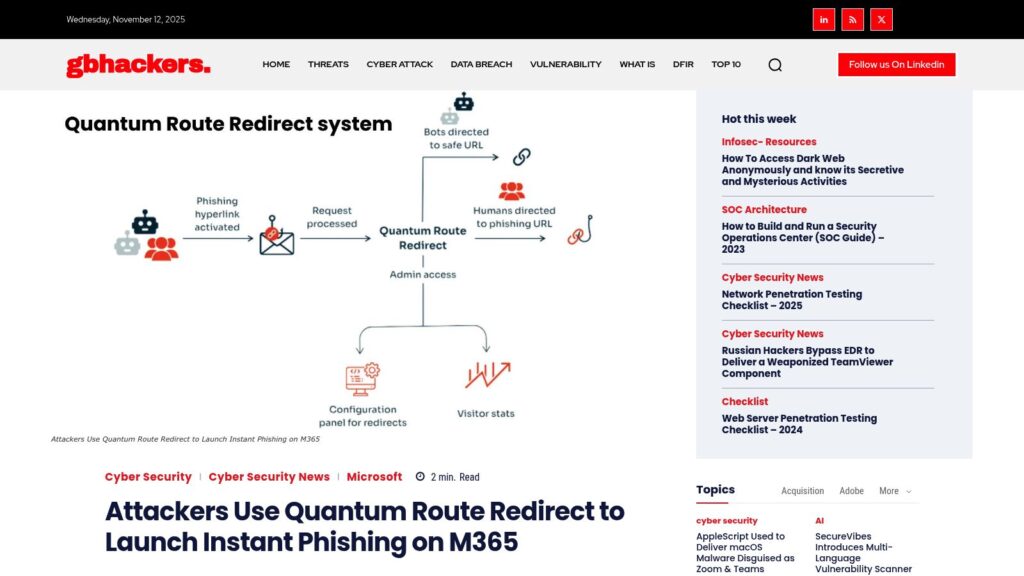
Quantum Route Redirect PhaaS Targets Microsoft 365 Users Worldwide

Quantum Route Redirect, a new phishing automation platform, uses around 1,000 domains to steal Microsoft 365 credentials, primarily targeting users in the U.S. It automates phishing attacks by routing victims to malicious sites through deceptive emails. The kit is designed for ease of use, even for less skilled attackers, and incorporates mechanisms to evade detection by automated security tools. Security analysts recommend implementing robust URL filtering to combat this threat.

https://www.bleepingcomputer.com/news/security/quantum-route-redirect-phaas-targets-microsoft-365-users-worldwide/

GlassWorm Malware Discovered in Three VS Code Extensions With Thousands of Installs

GlassWorm Malware targets VS Code via three malicious extensions, harvesting credentials and using invisible code to spread. Despite attempts to remove it, the campaign persists, affecting various regions, including government entities. The malware showcases evolving attack techniques, such as utilizing blockchain for command/control. Security researchers identified a Russian-speaking attacker behind it, indicating significant risks to organizations using affected tools.

https://thehackernews.com/2025/11/glassworm-malware-discovered-in-three.html

America’s Cybersecurity Defenses Are Cracking

CISA’s role in US cybersecurity is diminished due to staffing cuts, reassignments, and politicization, leading to a loss of trust among state officials like Arizona’s Secretary of State, who now hesitate to engage with the agency. This situation jeopardizes cybersecurity efforts, especially for critical infrastructure, as agencies are wary of sharing sensitive information. Historically, CISA provided vital support for election security and other sectors, but recent developments have created significant vulnerabilities in the nation’s defenses.

https://www.theverge.com/policy/816882/cisa-cybersecurity-elections-infrastructure-shutdown

Afterpay Confronts New Fraud Type

Fraudsters are colluding as fake merchants and consumers to exploit Afterpay’s buy now, pay later services, leading to significant losses. This emerging fraud type leverages synthetic identities and artificial intelligence to create false profiles. Experts warn that as buy now, pay later options expand to high-ticket items, such scams may increase, making it critical for payment services to enforce stringent checks on merchants.

https://www.paymentsdive.com/news/afterpay-confronts-new-fraud-type/805103/

Better Business Bureau Issues Warning About ‘ghost Tapping’ Scam. Here’s Why You May Not Even Be Aware if You’ve Been a Victim of This Trend

Ghost tapping scam exploits contactless payments. Scammers charge unsuspecting victims large amounts through “tap-to-pay” without consent. Methods include bumping into people or posing as vendors. Victims may not realize until seeing charges. Stay vigilant: use RFID-blocking wallets, verify merchants, enable transaction alerts, and report suspicious activity swiftly.

https://moneywise.com/news/better-business-bureau-issues-warning-about-ghost-tapping

5 Reasons Why Attackers Are Phishing Over LinkedIn

LinkedIn phishing is rising, with 34% of attacks occurring outside email. Key reasons include:

  1. Bypasses traditional security tools since LinkedIn DMs evade email security protections.
  2. Cheap and easy for attackers, leveraging legitimate account hijacking.
  3. Facilitates targeting high-value individuals due to easy reconnaissance.
  4. Users more likely to trust messages from familiar contacts.
  5. Potential rewards are high because breaches can compromise core business accounts and data.

Organizations must adapt security to guard against these threats across multiple channels, not just email.

https://www.bleepingcomputer.com/news/security/5-reasons-why-attackers-are-phishing-over-linkedin/

Scroll to Top