Can a Global, Decentralized System Save CVE Data?
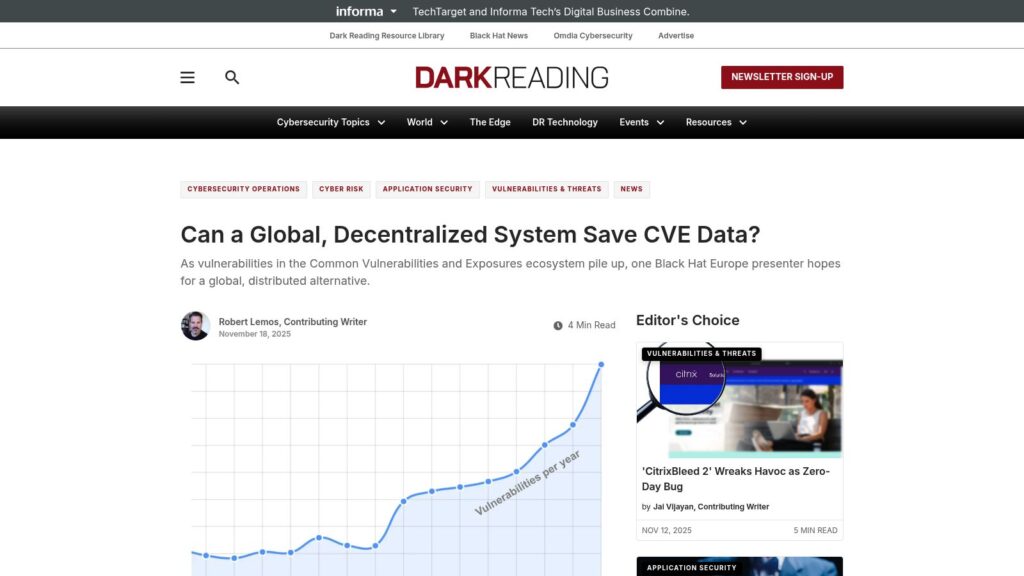
The NVD has struggled to keep up with the growing volume of CVE vulnerability disclosures, leading to backlogs and delays in data enrichment due to limited funding and staffing. Centralized management by U.S. entities such as NIST and MITRE creates a single point of failure, as a 2024 funding crisis highlighted. Security experts like Jerry Gamblin propose a decentralized system in which regional and industry leaders share responsibility and introduce redundancy, such as through the EUVD. The idea calls for globally standardized, uniquely identified records and broad industry participation, but remains an early-stage concept seeking engagement and feedback from the broader security community.

https://www.darkreading.com/cybersecurity-operations/can-global-decentralized-system-save-cve-data
Cloudflare Outage on November 18, 2025

On November 18, 2025, Cloudflare experienced a significant outage affecting core network traffic after a database permission change caused a feature file to double in size, leading to system failures. Initial suspicions of a DDoS attack were disproved as the issue was traced to bad configurations propagated throughout the network. The outage, which resulted in numerous HTTP 5xx error codes and impacted various services, was resolved by reverting to a stable configuration and restarting core proxies. Cloudflare acknowledged the unacceptable nature of the incident and committed to implementing measures to prevent future occurrences.

https://blog.cloudflare.com/18-november-2025-outage/

Microsoft: Azure Hit by 15 Tbps DDoS Attack Using 500,000 IP Addresses

Microsoft’s Azure was targeted by a 15.72 Tbps DDoS attack from the Aisuru botnet, utilizing over 500,000 IP addresses, and employing high-rate UDP floods, peaking at 3.64 billion packets per second. Aisuru, a Turbo Mirai-class botnet, exploits vulnerabilities in IoT devices, significantly growing in size after breaching a router firmware update server. This attack follows other DDoS incidents linked to the same botnet, and highlights ongoing security challenges with IoT devices.

https://www.bleepingcomputer.com/news/microsoft/microsoft-aisuru-botnet-used-500-000-ips-in-15-tbps-azure-ddos-attack/

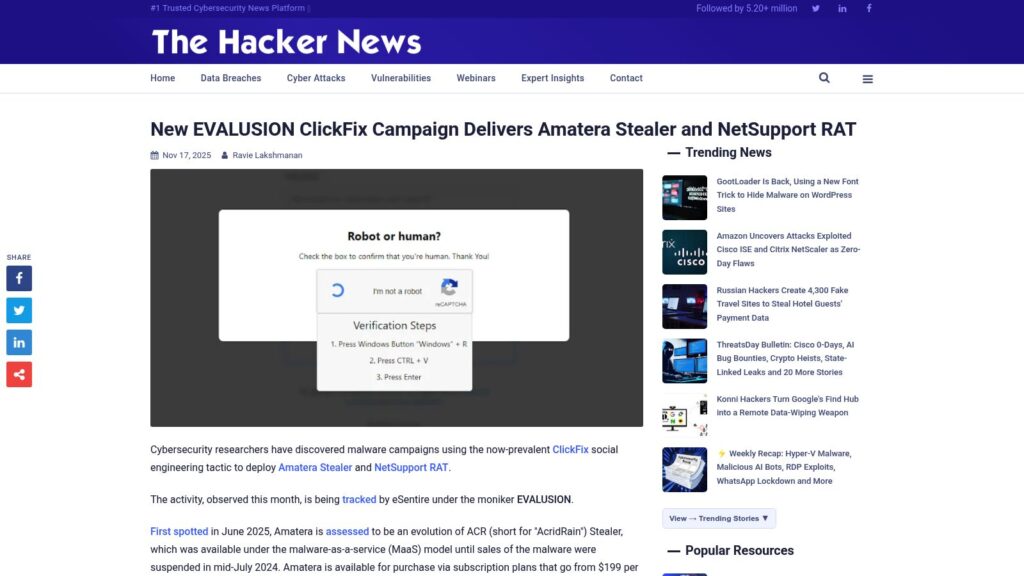
New EVALUSION ClickFix Campaign Delivers Amatera Stealer and NetSupport RAT

New EVALUSION campaign deploys Amatera Stealer and NetSupport RAT via ClickFix social engineering. Amatera targets sensitive data and circumvents security measures. Attackers trick users into executing malicious commands through fake reCAPTCHA pages, leading to data exfiltration. Various phishing tactics, including fake invoices and compromised sites, are used to spread malware.

https://thehackernews.com/2025/11/new-evalusion-clickfix-campaign.html

Dutch Police Seizes 250 Servers Used by “Bulletproof Hosting” Service

Dutch police seized 250 servers from a bulletproof hosting service used by cybercriminals for anonymity in illegal activities, including ransomware and phishing. This operation revealed significant connections to over 80 cybercrime investigations. The company promoted complete user anonymity and refused cooperation with law enforcement. A forensic analysis of the servers is underway to uncover more details about its operators and clients, though no arrests have been reported yet.

https://www.bleepingcomputer.com/news/security/dutch-police-seizes-250-servers-used-by-bulletproof-hosting-service/

Ransomware’s Fragmentation Reaches a Breaking Point While LockBit Returns

Ransomware landscape in Q3 2025 shows record fragmentation with 85 active groups and 1,590 victims. Despite law enforcement efforts, smaller, decentralized operations have emerged post-takedowns, reducing credibility in ransom payments. New brands like LockBit 5.0 highlight a potential return to centralization, increasing operational scale and trust. Ransomware tactics are evolving, making traditional tracking methods ineffective; analysts now need to monitor affiliate behavior and economic motivations to navigate the changing ecosystem.

https://thehackernews.com/2025/11/ransomwares-fragmentation-reaches.html

Increase in Lumma Stealer Activity Coincides With Use of Adaptive Browser Fingerprinting Tactics

Lumma Stealer, also known as Water Kurita, has resurfaced with new tactics after an initial drop in activity following the public disclosure of its core members’ identities. Since late October 2025, it has employed browser fingerprinting in conjunction with its traditional command-and-control approaches to evade detection, gather extensive data on the victim’s environment, and maintain operational continuity. The malware injects itself into trusted browser processes, collects detailed system and browser information via JavaScript, and sends this data back to its command-and-control (C&C) servers stealthily. Despite some operational setbacks and reduced public presence, Lumma Stealer remains active, with operators likely keeping a low profile to avoid further scrutiny. Organizations are advised to enhance email vigilance, restrict software installations, monitor for suspicious CAPTCHA behaviors, and utilize MFA, while Trend Vision One tools detect and aid in identifying relevant compromise indicators.

https://www.trendmicro.com/en_us/research/25/k/lumma-stealer-browser-fingerprinting.html

Logitech Data Breach — What We Know As 0-Day Hack Attack Confirmed

Logitech experienced a data breach after a Clop ransomware group attack that used a zero-day flaw in a third-party platform. The attack did not directly affect Logitech’s products or business operations, but it may have exposed limited employee, consumer, and supplier data. Logitech believes sensitive personal data was not compromised and has since patched the vulnerability. The firm is working with cybersecurity experts and believes that this incident won’t materially affect its finances due to insurance coverage. Experts stress that the incident highlights the risks associated with zero-day exploits and underscores the need for stronger security measures.

https://www.forbes.com/sites/daveywinder/2025/11/15/logitech-data-breach—what-we-know-as-0-day-hack-attack-confirmed/

Researchers Find Serious AI Bugs Exposing Meta, Nvidia, and Microsoft Inference Frameworks

AI Bugs Found in Major Frameworks: Researchers discovered serious vulnerabilities in AI inference frameworks by Meta, Nvidia, and Microsoft due to unsafe deserialization practices with ZeroMQ and Python’s pickle. These “ShadowMQ” flaws allow remote code execution across multiple projects from code reuse. Various identified vulnerabilities have potential CVSS scores from 6.3 to 8.8; the exploitation could lead to code execution and model theft. Cybersecurity solutions emphasize the need for correct coding practices and security audits amid rapid development.

https://thehackernews.com/2025/11/researchers-find-serious-ai-bugs.html

The Scammer Next Door — The Dial

India’s increasing fraud culture mirrors its stark inequality. A journalist recounts receiving a fake lottery call, leading to insights into a booming scam industry during the COVID-19 lockdown. Exposing the inner workings, she interviews scam operators like “Rana Pratap,” who leverage desperation and misinformation for profit. Amid mass unemployment, many view scamming as a viable career. The growth of scams reveals a collective disillusionment; ordinary citizens, driven by a deteriorating trust in traditional success paths, become scamming entrepreneurs, reflecting a troubling trend of deceit in society.

https://www.thedial.world/articles/news/india-scams-scamlands

Lawmakers Want to Ban VPNs—And They Have No Idea What They’re Doing

Lawmakers in Wisconsin and Michigan are attempting to ban Virtual Private Networks (VPNs) to enforce age verification, arguing it will protect children online. The bills propose that websites must block VPN users, which experts argue is technically infeasible and harmful to various user groups including businesses, students, and vulnerable populations seeking safety. The broad definition of “harmful to minors” in these laws could censor a wide range of expression and essential information. Critics emphasize that banning VPNs undermines privacy, creates data security risks, and fails to address the real issues affecting online safety. Overall, they urge lawmakers to reconsider such measures, which threaten digital freedom and privacy rights.

https://www.eff.org/deeplinks/2025/11/lawmakers-want-ban-vpns-and-they-have-no-idea-what-theyre-doing

Researchers Question Anthropic Claim That AI-assisted Attack Was 90% Autonomous

Researchers question Anthropic’s claim that a recent AI-assisted cyber attack was 90% autonomous, arguing the results aren’t as significant as presented. Despite using Claude AI to streamline tasks in targeted cyber espionage, success rates were low, with doubts about the real novelty of the techniques employed. The study reveals AI’s current limitations in cybersecurity applications and suggests mixed results compared to traditional methods.

https://arstechnica.com/security/2025/11/researchers-question-anthropic-claim-that-ai-assisted-attack-was-90-autonomous/

Phishing Tool Smart Redirects Bypass Email Security

Quantum Route Redirect is a new phishing tool that simplifies the creation of advanced phishing campaigns targeting Microsoft 365 users. Automating complex attack steps and utilizing smart redirects enables even low-skill attackers to bypass detection systems, redirecting security tools to legitimate pages while delivering phishing schemes to human users. The tool has a broad international impact, primarily affecting US victims, and can elude traditional and advanced email security measures. Defensive strategies include using advanced content analysis, URL filtering, and sandboxing technologies to identify and block such attacks.

https://www.darkreading.com/endpoint-security/phishing-tool-smart-redirects-bypass-email-security

Disrupting the First Reported AI-orchestrated Cyber Espionage Campaign Anthropic

AI orchestrated a sophisticated cyber espionage campaign, marking the first major attack with minimal human involvement. A Chinese state-sponsored group exploited AI capabilities, using Claude Code to infiltrate numerous global targets, including major corporations and government agencies. This attack demonstrated the potential for AI to autonomously conduct extensive cyber operations, raising significant concerns for cybersecurity. Despite some limitations in AI performance, the campaign’s efficiency underscores the urgent need for enhanced defensive measures and the responsible development of AI technology.

https://www.anthropic.com/news/disrupting-AI-espionage

Scroll to Top