Hackers Ramp up Scans for Leaked Git Tokens and Secrets

Hackers are increasing scans for leaked Git configuration files, which can expose sensitive data like tokens and credentials. A report by GreyNoise highlighted a surge in scans from April 20-21, 2025, with nearly 4,800 unique IPs detected, predominantly from Singapore, the U.S., and Germany. These exposed Git files often lead to significant security breaches, allowing unauthorized access to cloud services and repositories. To mitigate risks, experts recommend blocking access to .git/ directories and monitoring logs for suspicious activity.

https://www.bleepingcomputer.com/news/security/hackers-ramp-up-scans-for-leaked-git-tokens-and-secrets/

Hello 0-Days, My Old Friend: a 2024 Zero-Day Exploitation Analysis

Google’s Threat Intelligence Group reported 75 zero-day vulnerabilities exploited in 2024, down from 98 in 2023 but up from 63 in 2022. This year’s exploitation continued a trend towards targeting enterprise technologies over end-user products. Key findings included:

  1. Trends in Exploitation: 44% of vulnerabilities targeted enterprise software, up from 37% in 2023. Vendors are improving security, reducing exploits on popular targets like browsers.
  2. Notable Targets: Security and networking products saw increased exploitation, with a significant focus on Ivanti and Palo Alto. Attackers’ focus is shifting from end-user devices to critical enterprise infrastructures.
  3. Actor Analysis: State-sponsored espionage actors, particularly from China and North Korea, accounted for the majority of attributable exploitation, often blending espionage with financial motives.
  4. Exploited Vulnerability Types: The most common were remote code execution and privilege escalation vulnerabilities, often resulting from software coding errors.

Overall, while detection and vendor defenses improve, zero-day vulnerabilities remain appealing to threat actors, necessitating stronger vendor security practices.

https://cloud.google.com/blog/topics/threat-intelligence/2024-zero-day-trends/

Cybersecurity Vendors Are Themselves Under Attack by Hackers, SentinelOne Says

Cybersecurity firms like SentinelOne face significant threats from hackers, including ransomware and state-sponsored attacks from China and North Korea. Despite their role in protecting clients, they are prime targets due to their access and insights into many systems. A recent report highlighted the taboo around discussing such attacks within the industry, as companies feel uncomfortable admitting vulnerabilities.

https://cyberscoop.com/cybersecurity-vendors-are-under-attack-sentinelone-says/

Three Ways AI Can Weaken Your Cybersecurity

AI can weaken cybersecurity through three main methods:

  1. Slopsquatting – Spreading malware via hallucinated software libraries recommended by AI, often targeting users who mistype URLs.
  2. Prompt Injection – Attackers inject malicious prompts into AI applications, potentially leading to unauthorized information access or code execution.
  3. Data Poisoning – Manipulating training data to skew AI model outputs, which poses risks for various industries.

These tactics exploit the vulnerabilities of AI systems, emphasizing the need for increased vigilance and adapted security measures.

https://www.bigdatawire.com/2025/04/25/three-ways-ai-can-weaken-your-cybersecurity/

DragonForce Expands Ransomware Model With White-label Branding Scheme

DragonForce expands ransomware model by forming a cartel structure, allowing affiliates to use its malware and branding without managing infrastructure. Affiliates pay a 20% fee on ransoms and must adhere to specific rules. The group, claiming to avoid targeting certain healthcare entities, aims to attract less technical actors and increase profits through flexibility in deploying ransomware under various brands.

https://www.bleepingcomputer.com/news/security/dragonforce-expands-ransomware-model-with-white-label-branding-scheme/

RSAC 2025: What We Expect at the Largest Cybersecurity Conference of the Year

RSAC 2025, the largest cybersecurity conference, will address critical topics like AI management, non-human identities, and online safety for seniors. Attendees will learn from experts including Bruce Schneier on AI trustworthiness, and explore scam prevention strategies led by Ayelet Biger-Levin. Key initiatives include evolving the web for privacy with Sir Tim Berners-Lee’s Solid project and a special DARPA AI challenge showcase. PCMag will cover highlights from the event starting April 28.

https://uk.pcmag.com/security/157731/rsac-2025-what-we-expect-at-the-largest-cybersecurity-conference-of-the-year

Behavioural Biometrics Seen as Key Layer, Not Replacement for Passwords

Behavioural biometrics enhance security as a complementary layer to passwords, not a replacement. They analyze unique user interactions continuously, improving identification and reducing fraud risk. AI integration allows adaptation to user behavior, while offering a seamless experience. Limitations include potential false rejections and privacy concerns. They’re seen as part of multi-factor authentication frameworks, with strong password security remaining essential. Banks illustrate their function as a background security layer alongside traditional methods.

https://securitybrief.co.uk/story/behavioural-biometrics-seen-as-key-layer-not-replacement-for-passwords

Hackers Can Now Bypass Linux Security Thanks to Terrifying New Curing Rootkit

New Curing rootkit exploits io_uring in Linux, bypassing traditional security tools by avoiding monitored system calls. This vulnerability poses significant risks, especially for cloud-native businesses. ARMO’s solution can mitigate this threat by managing system calls. Users relying solely on classic monitoring may be vulnerable.

https://betanews.com/2025/04/24/hackers-bypass-linux-security-with-armo-curing-rootkit/

Ransomware Now Plays a Role in Nearly Half of All Breaches, New Research Finds

Ransomware involved in 44% of data breaches in 2024, per Verizon’s report, showing a rise from one-third in 2023. Victims refusing to pay ransoms grew to 64%, and median ransom decreased to $115,000. Small businesses are hit hardest, facing ransomware in 88% of breaches. Overall, ransomware attacks are increasing across sectors, including finance and government.

https://therecord.media/ransomware-in-half-of-all-data-breaches-verizon

Threat Groups Exploit Resurgent Vulnerabilities

Threat groups increasingly exploit older vulnerabilities in edge devices, particularly VPNs and routers, according to GreyNoise research. Over half of these vulnerabilities, including Black Swan ones, are neglected due to lack of patches and outdated infrastructure, allowing attackers to easily weaponize them. In 2024, 40% of vulnerabilities exploited were from 2020 or earlier, indicating ongoing risks from unaddressed CVEs.

https://www.cybersecuritydive.com/news/threat-groups-exploiting-vulnerabilities/746229/

Ransomware Groups Test New Business Models to Hit More Victims, Increase Profits

Ransomware groups like DragonForce and Anubis are adopting new business models to attract affiliates and boost profits. DragonForce has rebranded as a “cartel,” allowing affiliates to create their own brands while using shared infrastructure, increasing potential risks. Anubis offers varied monetization schemes for affiliates and employs aggressive tactics to pressure victims into paying, including threats to publish data. The evolution of these models follows disruptions in the ransomware landscape, highlighting ongoing experimentation that could reshape the ecosystem. Despite a decrease in extortion payments, experts warn that the threat remains high with evolving vulnerabilities.

https://therecord.media/ransomware-groups-test-new-business-models-dragonforce-anubis

SuperCard X Android Malware Enables Contactless ATM and PoS Fraud Via NFC Relay Attacks

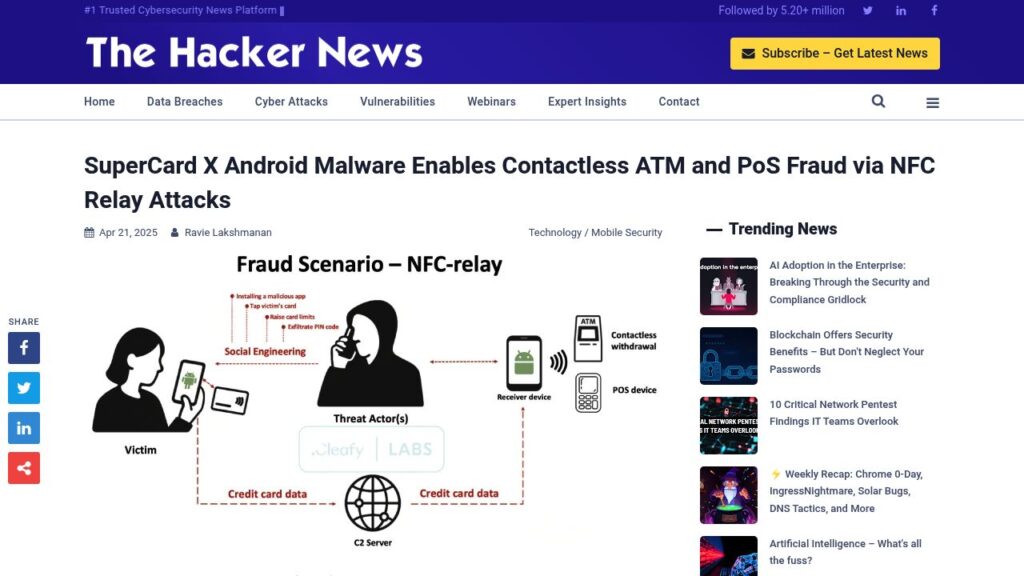
SuperCard X is a new Android malware platform enabling NFC relay attacks, allowing criminals to commit ATM and PoS fraud by intercepting and relaying card details. Targeting Italian banking customers, it employs social engineering tactics through fake apps and deceptive messages that prompt victims to install malicious software. The malware captures card data and relays it to external servers for unauthorized transactions. SuperCard X utilizes sophisticated techniques, including custom app versions and secure communication methods, posing significant financial risks to payment systems. Users are urged to avoid unknown apps and enable protections against malware.

https://thehackernews.com/2025/04/supercard-x-android-malware-enables.html

Apple Fixes Two Zero-days Exploited in Targeted iPhone Attacks

Apple patched two zero-day vulnerabilities in iPhones, affecting several operating systems, after reports of exploitation in targeted attacks. The flaws, found in CoreAudio and RPAC, allow remote code execution and bypass security features. Users are urged to update their devices immediately. This marks the fifth zero-day fix from Apple this year.

https://www.bleepingcomputer.com/news/security/apple-fixes-two-zero-days-exploited-in-targeted-iphone-attacks/

The Rise of Slopsquatting: How AI Hallucinations Are Fueling…

Slopsquatting is a new supply chain attack using AI-generated nonexistent package names, making it easier for attackers to exploit developer trust in AI tools. Research shows significant hallucination rates in code generation models, with 19.7% of suggested packages being fake. This poses serious risks as developers may unknowingly install these malicious packages, especially with the growing trend of “vibe coding” where developers rely heavily on AI for code creation. Security measures must adapt to identify and mitigate these threats effectively to protect software ecosystems.

https://socket.dev/blog/slopsquatting-how-ai-hallucinations-are-fueling-a-new-class-of-supply-chain-attacks

Scroll to Top