malware

New macOS Stealer Campaign Uses Script Editor in ClickFix Attack
A new macOS malware campaign delivering the Atomic Stealer exploits the built-in Script Editor app via a variation of the ClickFix attack, tricking users into running malicious scripts without manual Terminal interaction. The attack uses fake Apple-themed websites that launch Script Editor with pre-filled code to download and execute obfuscated payloads, targeting sensitive data such as Keychain items, browser passwords, and cryptocurrency wallets. Mac users are advised to treat Script Editor prompts with caution and rely only on official Apple documentation for system guidance.
https://www.bleepingcomputer.com/news/security/new-macos-stealer-campaign-uses-script-editor-in-clickfix-attack/

Axios Compromised on npm – Malicious Versions Drop Remote Access Trojan

The popular JavaScript HTTP client library, axios, was compromised on npm with malicious versions 1.14.1 and 0.30.4, injecting a hidden dependency, [email protected], which executes a postinstall script that drops a cross-platform remote access trojan (RAT). This sophisticated supply chain attack hijacked a maintainer's npm account to publish poisoned releases that contact a command-and-control server, deploy platform-specific payloads, self-delete to avoid detection, and were detected by StepSecurity’s tools, with remediation guidance provided.

https://www.stepsecurity.io/blog/axios-compromised-on-npm-malicious-versions-drop-remote-access-trojan

Stryker Rules Out Ransomware, Confirms Threat Actor Used Non-Propagating Malicious File

Medical technology company Stryker confirmed that its recent cybersecurity incident did not involve ransomware but rather a non-propagating malicious file used by threat actors to conceal activity within its systems. The company, working with Palo Alto Networks' Unit 42 and government agencies, stated the breach is contained with no evidence of impact on customers, suppliers, or partners, and prioritized restoring operations while continuing investigations.

https://industrialcyber.co/medical/stryker-rules-out-ransomware-confirms-threat-actor-used-non-propagating-malicious-file/

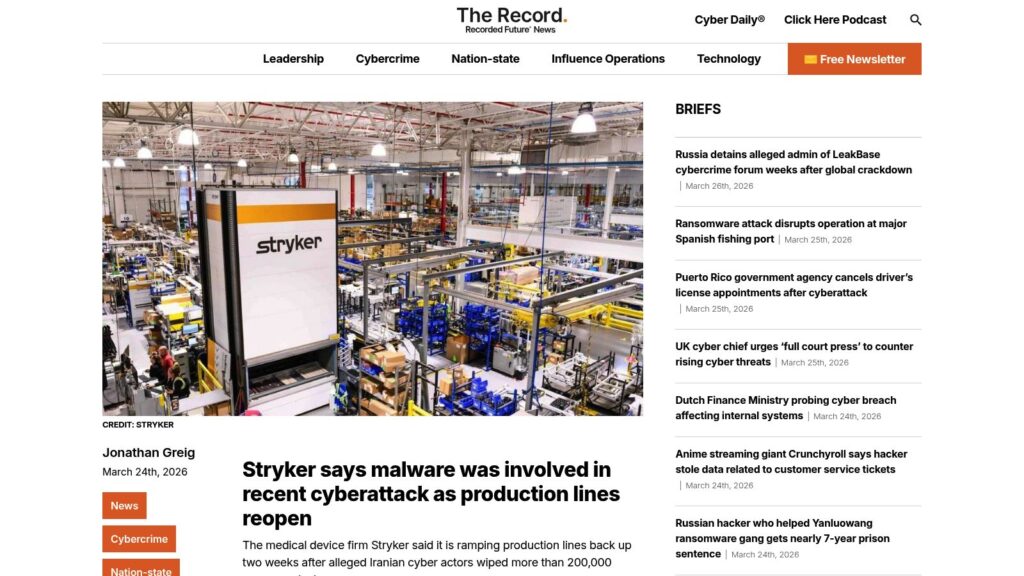
Stryker Says Malware Was Involved in Recent Cyberattack as Production Lines Reopen

Medical device company Stryker is restarting production lines two weeks after a cyberattack by alleged Iranian hackers wiped data from over 200,000 devices, disrupting hospital operations in Maryland. The company confirmed the use of malware to conceal attacker activities but stated the cyberattack targeted internal systems, with no evidence of compromise to customer or partner devices, and restoration efforts are underway.

https://therecord.media/stryker-cyberattack-malware-iran

Tycoon2FA Phishing Platform Returns After Recent Police Disruption

The Tycoon2FA phishing-as-a-service platform, disrupted by Europol and partners through the seizure of 330 domains in early March 2026, has quickly resumed operations to pre-disruption levels. Despite the takedown, CrowdStrike observed a rapid recovery using largely unchanged tactics, highlighting that without arrests or physical seizures, cybercriminals can swiftly restore their infrastructure due to continued demand in the phishing ecosystem.

https://www.bleepingcomputer.com/news/security/tycoon2fa-phishing-platform-returns-after-recent-police-disruption/

New “Darksword” iOS Exploit Used in Infostealer Attack on iPhones

The new DarkSword iOS exploit kit targets iPhones running iOS versions 18.4 to 18.7 and has been used since November 2025 to steal extensive personal data, including cryptocurrency wallet information, through malware families like GHOSTBLADE, GHOSTKNIFE, and GHOSTSABER. Discovered by Lookout and analyzed in cooperation with Google Threat Intelligence and iVerify, DarkSword exploits known vulnerabilities patched in the latest iOS releases, and its attacks begin via compromised websites injecting malicious iframes into the Safari browser to execute code that exfiltrates sensitive information. Users are advised to update to the latest iOS version and enable Lockdown Mode if at high risk.

https://www.bleepingcomputer.com/news/security/new-darksword-ios-exploit-used-in-infostealer-attack-on-iphones/

LeakNet Ransomware Uses ClickFix Via Hacked Sites, Deploys Deno In-Memory Loader

LeakNet ransomware uses the ClickFix social engineering tactic to trick users into running malicious commands via compromised websites as an initial access method. This approach allows LeakNet to bypass traditional methods and reduce costs. The ransomware also employs a Deno-based loader to execute payloads in memory, minimizing detection.

https://thehackernews.com/2026/03/leaknet-ransomware-uses-clickfix-via.html

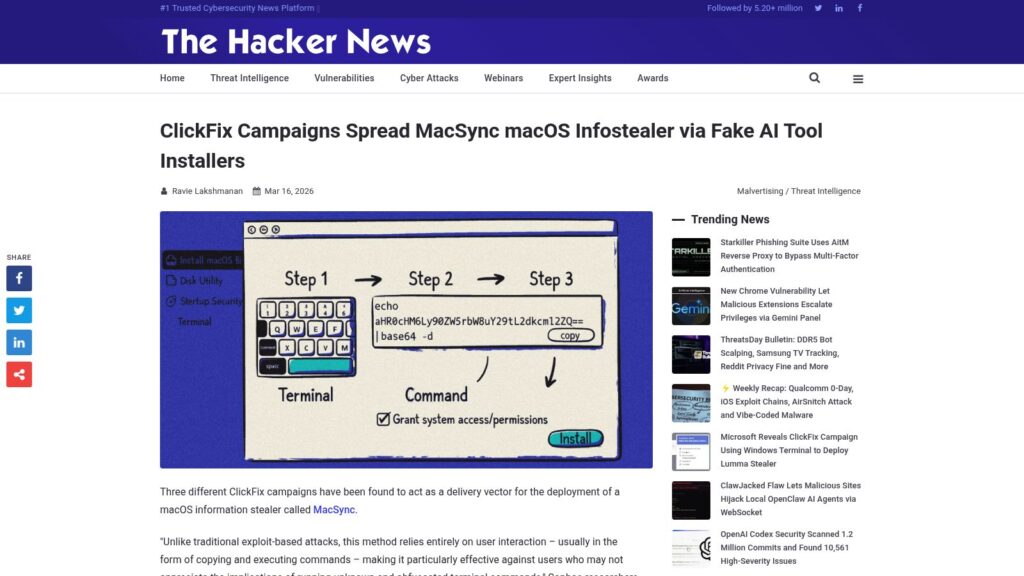
ClickFix Campaigns Spread MacSync macOS Infostealer Via Fake AI Tool Installers

Multiple ClickFix campaigns have been identified spreading the MacSync macOS information stealer through fake AI tool installers that trick users into running malicious Terminal commands. These campaigns leverage malvertising and social engineering, often using trusted platforms and search ads to lure victims, with recent variants employing advanced evasion techniques to harvest sensitive data like credentials and cryptocurrency wallet seed phrases. Security experts warn that these evolving tactics exploit developers’ trust in command-line installs and have been adopted by multiple threat actors targeting both macOS and Windows environments.

https://thehackernews.com/2026/03/clickfix-campaigns-spread-macsync-macos.html

InstallFix: Weaponizing Malvertized Install Guides

Attackers are using a technique called InstallFix, a social engineering attack where they clone installation pages of legitimate CLI tools and present victims with malicious install commands disguised as the real thing. This technique is particularly effective because it exploits the common practice of copying and pasting installation commands from websites, bypassing traditional security controls like email filtering. The attackers are using malvertising, specifically sponsored search results on Google, to distribute these fake installation pages, targeting popular tools like Claude Code.

https://pushsecurity.com/blog/installfix/

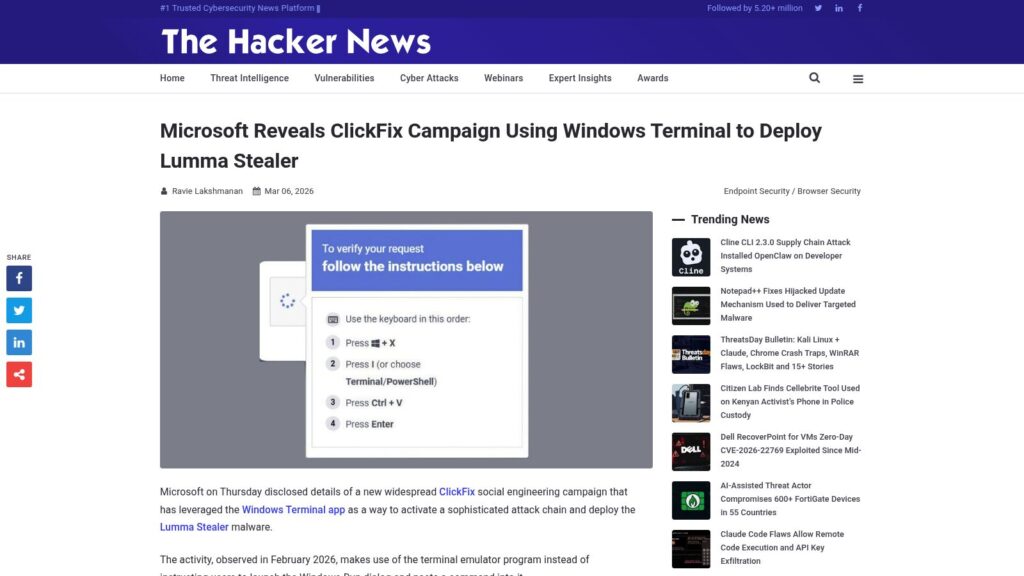
Microsoft Reveals ClickFix Campaign Using Windows Terminal to Deploy Lumma Stealer

Microsoft revealed a new phishing campaign, ClickFix, using Windows Terminal to deploy Lumma Stealer malware. The campaign tricks users into executing commands via a trusted app, bypassing detection methods aimed at the Run dialog. It executes a multi-stage attack: downloading and extracting malicious scripts, collecting credentials from browsers, and establishing persistence. The malware targets sensitive data, emphasizing the risks of social engineering tactics in cybersecurity.

https://thehackernews.com/2026/03/microsoft-reveals-clickfix-campaign.html

Coruna: The Mysterious Journey of a Powerful iOS Exploit Kit

Google's Threat Intelligence Group identified a new iOS exploit kit, “Coruna,” targeting iPhone models from iOS 13.0 to 17.2.1. Coruna comprises five exploit chains and uses advanced techniques to bypass mitigations. It was initially discovered with links to commercial surveillance, later leveraged by Russian espionage and Chinese financial criminals. Users are urged to update their devices to the latest iOS version or enable Lockdown Mode for security. The kit features sophisticated mechanisms for targeting and data theft, indicating a growing market for reused zero-day exploits.

https://cloud.google.com/blog/topics/threat-intelligence/coruna-powerful-ios-exploit-kit

APT36: a Nightmare of Vibeware

APT36, known as Transparent Tribe, shifts from conventional malware to “vibeware,” an AI-generated model producing numerous low-quality implants using niche languages like Nim, Zig, and Crystal. This evolution aims to evade detection and employs trusted cloud services for command and control. Despite technical flaws leading to ineffective malware, this model's production volume overwhelms defenses, indicating a trend towards automated, high-volume cyberattacks. Their targeted attacks focus on the Indian government, utilizing sophisticated social engineering tactics and established frameworks alongside new, poorly coded variants. Overall, APT36 embraces a strategy of integrating AI into malware design, resulting in mass-produced threats lacking true innovation but full of operational risk.

https://businessinsights.bitdefender.com/apt36-nightmare-vibeware

Malicious OpenClaw Skills Used to Distribute Atomic macOS Stealer

A new variant of Atomic macOS Stealer (AMOS) is being distributed through malicious OpenClaw skills, exploiting AI agentic workflows to trick users into installing the malware. The malware, disguised as a harmless skill, uses a fake dialogue box to request the user’s password and then exfiltrates sensitive data, including Apple and KeePass keychains, user documents, and system information. TrendAI™ Managed Detection and Response (MDR) customers are protected from this threat.

https://www.trendmicro.com/en_us/research/26/b/openclaw-skills-used-to-distribute-atomic-macos-stealer.html

Fake Zoom Meeting “Update” Silently Installs Surveillance Software

Fake Zoom meeting website installs surveillance software, Teramind, on Windows without user consent. Visitors encounter a fraudulent Zoom interface that prompts an automatic update, leading to malicious file download. The stealthily installed software monitors user activity without knowledge, resembling legitimate business surveillance tools. Users are advised not to open suspicious files from the site and to check for unauthorized installations. This exploit illustrates the rising trend of attackers using legitimate software for illicit purposes.

https://www.malwarebytes.com/blog/scams/2026/02/fake-zoom-meeting-update-silently-installs-surveillance-software

Facebook Ads Spread Fake Windows 11 Downloads That Steal Passwords and Crypto Wallets

Malicious Facebook ads mimicking Microsoft promote fake Windows 11 downloads, leading users to download malware instead of updates. This malware stealthily collects passwords and cryptocurrency data. It employs sophisticated evasion techniques, targeting regular users while avoiding detection by security systems. If affected, users should avoid logging in to accounts, scan their devices, change passwords on a secure device, and take precautions with any financial information. Security teams are advised to block phishing domains and monitor for specific malware signatures.

https://www.malwarebytes.com/blog/scams/2026/02/facebook-ads-spread-fake-windows-11-downloads-that-steal-passwords-and-crypto-wallets

Scroll to Top