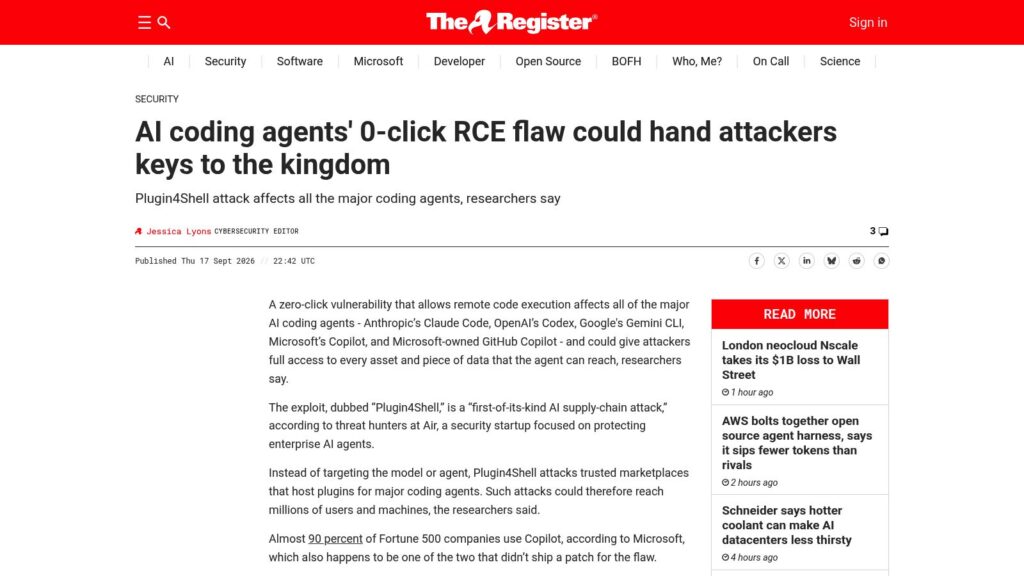
A zero-click remote code execution vulnerability called Plugin4Shell affects major AI coding agents—including Anthropic’s Claude Code, OpenAI’s Codex, Google’s Gemini CLI, and Microsoft’s Copilot—by exploiting a flaw in how these agents enforce SHA-pinning for marketplace plugins. This supply-chain attack allows attackers to replace trusted plugins with malicious versions without user interaction, potentially granting full access to affected systems. While Anthropic and OpenAI have patched the flaw, Google and Microsoft have not fully addressed it, leaving users vulnerable.
AI Coding Agents’ 0-Click RCE Flaw Could Hand Attackers Keys to the Kingdom