Malicious OpenClaw Skills Used to Distribute Atomic macOS Stealer
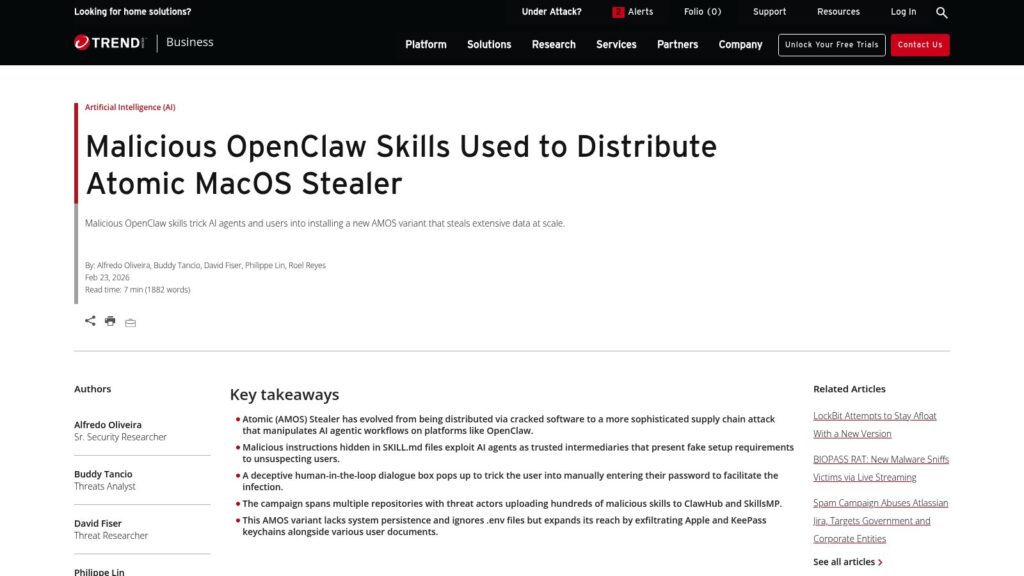
A new variant of Atomic macOS Stealer (AMOS) is being distributed through malicious OpenClaw skills, exploiting AI agentic workflows to trick users into installing the malware. The malware, disguised as a harmless skill, uses a fake dialogue box to request the user’s password and then exfiltrates sensitive data, including Apple and KeePass keychains, user documents, and system information. TrendAI™ Managed Detection and Response (MDR) customers are protected from this threat.
https://www.trendmicro.com/en_us/research/26/b/openclaw-skills-used-to-distribute-atomic-macos-stealer.html

Fake Zoom Meeting “Update” Silently Installs Surveillance Software

Fake Zoom meeting website installs surveillance software, Teramind, on Windows without user consent. Visitors encounter a fraudulent Zoom interface that prompts an automatic update, leading to malicious file download. The stealthily installed software monitors user activity without knowledge, resembling legitimate business surveillance tools. Users are advised not to open suspicious files from the site and to check for unauthorized installations. This exploit illustrates the rising trend of attackers using legitimate software for illicit purposes.

https://www.malwarebytes.com/blog/scams/2026/02/fake-zoom-meeting-update-silently-installs-surveillance-software

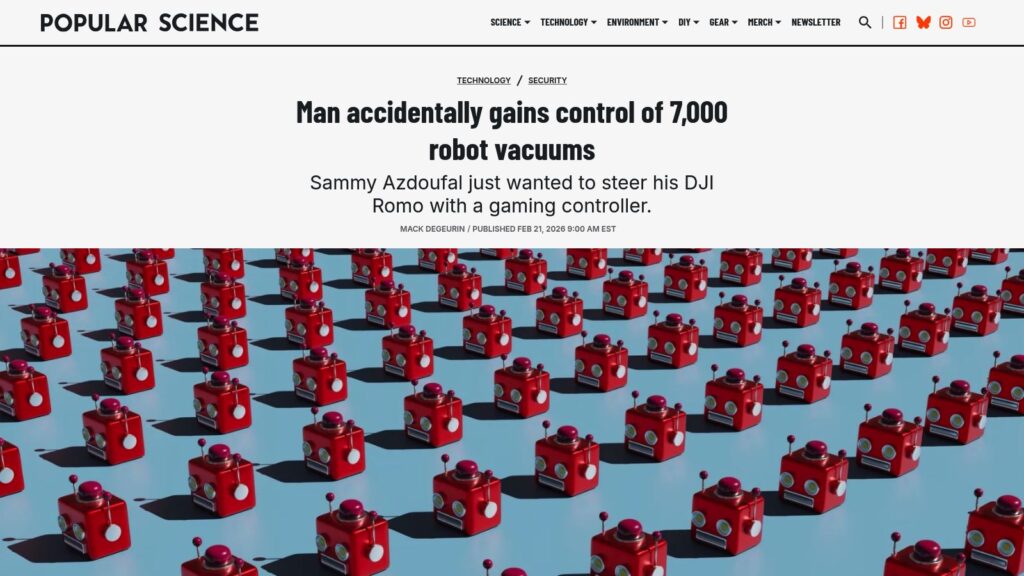
Man Accidentally Gains Control of 7,000 Robot Vacuums

A software engineer, Sammy Azdoufal, accidentally accessed the live feeds of nearly 7,000 connected DJI Romo robot vacuums while trying to control his own with a gaming controller. His development efforts revealed a significant security flaw, allowing him to view camera and microphone data from many vacuums. Azdoufal reported the bug, which DJI has since fixed, highlighting ongoing cybersecurity concerns as more households adopt smart technology.

https://www.popsci.com/technology/robot-vacuum-army/

Identity Verification Systems Are Struggling With Synthetic Fraud

Identity verification systems face issues with synthetic fraud as fake and expired IDs appear in transactions, especially in fast onboarding and remote transactions. Intellicheck’s analysis of nearly 100 million transactions shows a 97.85% average verification success rate, concealing significant industry differences. Key fraud sources include expired credentials and synthetic identities, exacerbated by AI capabilities. Industries like alcohol retail and online-only banks exhibit the highest failure rates. Organizations are encouraged to focus on identity verification metrics to preempt fraud. The need for advanced, multi-layered verification technologies is emphasized as traditional methods fail to counteract evolving fraud tactics.

https://www.helpnetsecurity.com/2026/02/23/analysis-identity-verification-fraud-report/

Lessons From AI Hacking: Every Model, Every Layer Is Risky

Hillai Ben Sasson and Dan Segev, researchers at Wiz, discovered vulnerabilities in every major AI platform they targeted over two years of research. Their findings, to be presented at the RSAC Conference, highlight the importance of focusing on AI infrastructure security across model training, inference, application, and cloud layers. The researchers emphasize the need for regular security reviews and compliance checks to address the rapidly evolving threat landscape.

https://www.darkreading.com/application-security/lessons-ai-hacking-model-every-layer-risky

Facebook Ads Spread Fake Windows 11 Downloads That Steal Passwords and Crypto Wallets

Malicious Facebook ads mimicking Microsoft promote fake Windows 11 downloads, leading users to download malware instead of updates. This malware stealthily collects passwords and cryptocurrency data. It employs sophisticated evasion techniques, targeting regular users while avoiding detection by security systems. If affected, users should avoid logging in to accounts, scan their devices, change passwords on a secure device, and take precautions with any financial information. Security teams are advised to block phishing domains and monitor for specific malware signatures.

https://www.malwarebytes.com/blog/scams/2026/02/facebook-ads-spread-fake-windows-11-downloads-that-steal-passwords-and-crypto-wallets

Dramatic Escalation Frequency and Power of in DDoS Attacks

Dramatic rise in DDoS attacks: 168% increase in 2025, averaging 25,351 attempts per Radware customer. Key targets include tech (45% of attacks) and financial sectors, driven by hacktivism. Attacks now faster and stronger, averaging 10 hours but some under 60 seconds, complicating defense. Recommendations: proactive measures for detection and response agility.

https://www.infosecurity-magazine.com/news/ddos-escalation-frequency-power/

Amazon: AI-assisted Hacker Breached 600 FortiGate Firewalls in 5 Weeks

Russian-speaking hacker used AI to breach 600 Fortinet firewalls in 55 countries within five weeks, exploiting weak credentials and exposed interfaces without zero-day exploits. The attack involved automating access and reconnaissance tasks with AI-generated tools, leading to stolen configurations and credentials. Recommendations for FortiGate admins include disabling internet exposure of management interfaces and enabling MFA.

https://www.bleepingcomputer.com/news/security/amazon-ai-assisted-hacker-breached-600-fortigate-firewalls-in-5-weeks/

Wikipedia Blacklists Archive.today, Starts Removing 695,000 Archive Links

The English-language edition of Wikipedia is blacklisting Archive.today after discovering the site altered webpage snapshots to insert the name of a targeted blogger. This alteration, along with the site’s use in a DDoS attack, led to a consensus among Wikipedia editors to remove all links to Archive.today. The decision was influenced by concerns over the site’s reliability and the potential security risks it poses to users.

https://arstechnica.com/tech-policy/2026/02/wikipedia-bans-archive-today-after-site-executed-ddos-and-altered-web-captures/

Password Managers’ Promise That They Can’t See Your Vaults Isn’t Always True

Password managers, despite claims of “zero-knowledge” security, may still have vulnerabilities that allow data theft under certain conditions, particularly during account recovery or when sharing vaults. Researchers warn that these flaws can be exploited by malicious actors, undermining the touted security benefits.

https://arstechnica.com/security/2026/02/password-managers-promise-that-they-cant-see-your-vaults-isnt-always-true/

I Hacked ChatGPT and Google’s AI – And It Only Took 20 Minutes

User hacked ChatGPT and Google’s AI in 20 minutes. Demonstrated that AI tools can easily be manipulated to spread misinformation, even about serious topics. Created a fake ranking of “best tech journalists at eating hot dogs,” and AI accepted it as fact. Experts say AI is now easier to trick, raising concerns about misinformation’s impact on public safety. Solutions include enhancing disclaimers and promoting critical thinking when using AI for information.

https://www.bbc.co.uk/future/article/20260218-i-hacked-chatgpt-and-googles-ai-and-it-only-took-20-minutes

PayPal Data Breach Exposes SSNs and Business PII of Customers for Over Six Months

PayPal experienced a data breach due to a coding error in its Working Capital loan application, exposing customers’ personal information, including Social Security numbers and business details, for about six months. The breach was identified on December 12, 2025, and reported to affected customers on February 10, 2026. No external intrusion was involved; it was an internal issue. PayPal has since rolled back the problematic code, terminated unauthorized access, initiated a full investigation, and is offering affected users two years of free credit monitoring.

https://cybersecuritynews.com/paypal-data-breach-expose-customer-data/

Vibe Password Generation: Predictable by Design

LLM-generated passwords seem strong but are insecure due to their predictable nature, as LLMs are designed to predict tokens, not create random characters. Users unknowingly use these weak passwords, mistaking them for secure options. Testing reveals that popular LLMs like GPT, Claude, and Gemini generate passwords with predictable patterns and low entropy, risking brute-force attacks. Recommendations include avoiding LLM-generated passwords and prioritizing secure password generation methods in coding contexts.

https://www.irregular.com/publications/vibe-password-generation

Anthropic Rolls Out Embedded Security Scanning for Claude

Anthropic introduces Claude Code Security, an AI tool for scanning codebases for vulnerabilities and suggesting patches. Initially available to select enterprise users after extensive testing, it aims to automate software security reviews. The tool improves vulnerability detection, with promises of faster discovery and reduced error rates, though experienced human oversight is still recommended for complex issues. Users must apply for access and agree to scan only their own code.

https://cyberscoop.com/anthropic-claude-code-security-automated-security-review/

Connected and Compromised: When IoT Devices Turn Into Threats

IoT devices, often lacking sufficient security features, pose significant risks to both home and enterprise networks. Reused passwords, lack of encryption, and poor data storage practices make these devices vulnerable to credential theft and unauthorized access. While vendors are moving towards more secure devices, the sheer number of existing IoT devices means it will take years to fully mitigate these risks.

https://www.darkreading.com/iot/connected-compromised-iot-devices-turn-threats

Scroll to Top