The Scammer Next Door — The Dial

India's increasing fraud culture mirrors its stark inequality. A journalist recounts receiving a fake lottery call, leading to insights into a booming scam industry during the COVID-19 lockdown. Exposing the inner workings, she interviews scam operators like “Rana Pratap,” who leverage desperation and misinformation for profit. Amid mass unemployment, many view scamming as a viable career. The growth of scams reveals a collective disillusionment; ordinary citizens, driven by a deteriorating trust in traditional success paths, become scamming entrepreneurs, reflecting a troubling trend of deceit in society.

https://www.thedial.world/articles/news/india-scams-scamlands
Lawmakers Want to Ban VPNs—And They Have No Idea What They’re Doing

Lawmakers in Wisconsin and Michigan are attempting to ban Virtual Private Networks (VPNs) to enforce age verification, arguing it will protect children online. The bills propose that websites must block VPN users, which experts argue is technically infeasible and harmful to various user groups including businesses, students, and vulnerable populations seeking safety. The broad definition of “harmful to minors” in these laws could censor a wide range of expression and essential information. Critics emphasize that banning VPNs undermines privacy, creates data security risks, and fails to address the real issues affecting online safety. Overall, they urge lawmakers to reconsider such measures, which threaten digital freedom and privacy rights.

https://www.eff.org/deeplinks/2025/11/lawmakers-want-ban-vpns-and-they-have-no-idea-what-theyre-doing

Researchers Question Anthropic Claim That AI-assisted Attack Was 90% Autonomous

Researchers question Anthropic's claim that a recent AI-assisted cyber attack was 90% autonomous, arguing the results aren't as significant as presented. Despite using Claude AI to streamline tasks in targeted cyber espionage, success rates were low, with doubts about the real novelty of the techniques employed. The study reveals AI’s current limitations in cybersecurity applications and suggests mixed results compared to traditional methods.

https://arstechnica.com/security/2025/11/researchers-question-anthropic-claim-that-ai-assisted-attack-was-90-autonomous/

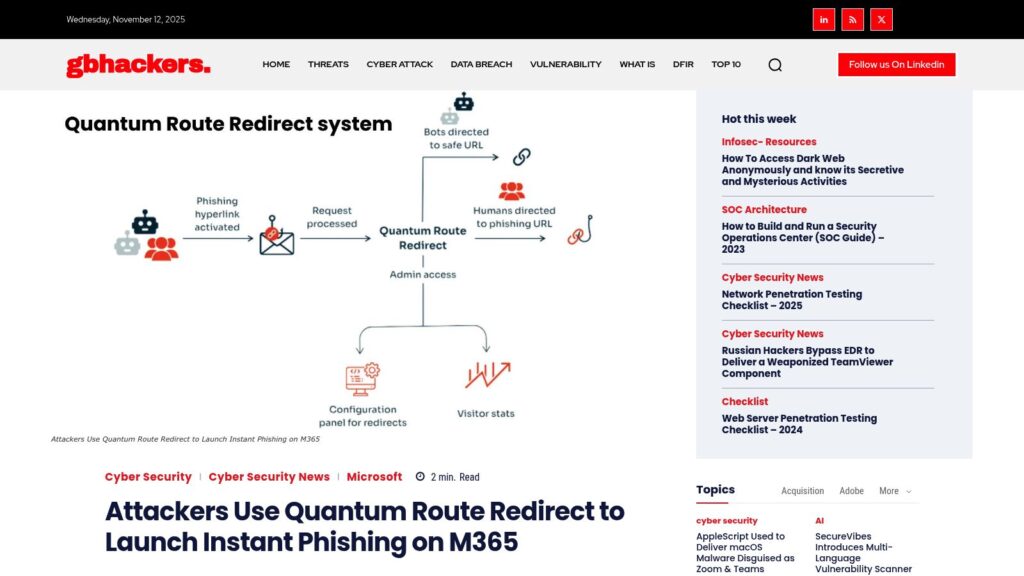
Phishing Tool Smart Redirects Bypass Email Security

Quantum Route Redirect is a new phishing tool that simplifies the creation of advanced phishing campaigns targeting Microsoft 365 users. Automating complex attack steps and utilizing smart redirects enables even low-skill attackers to bypass detection systems, redirecting security tools to legitimate pages while delivering phishing schemes to human users. The tool has a broad international impact, primarily affecting US victims, and can elude traditional and advanced email security measures. Defensive strategies include using advanced content analysis, URL filtering, and sandboxing technologies to identify and block such attacks.

https://www.darkreading.com/endpoint-security/phishing-tool-smart-redirects-bypass-email-security

Disrupting the First Reported AI-orchestrated Cyber Espionage Campaign Anthropic

AI orchestrated a sophisticated cyber espionage campaign, marking the first major attack with minimal human involvement. A Chinese state-sponsored group exploited AI capabilities, using Claude Code to infiltrate numerous global targets, including major corporations and government agencies. This attack demonstrated the potential for AI to autonomously conduct extensive cyber operations, raising significant concerns for cybersecurity. Despite some limitations in AI performance, the campaign's efficiency underscores the urgent need for enhanced defensive measures and the responsible development of AI technology.

https://www.anthropic.com/news/disrupting-AI-espionage

Breaking: Google Is Easing up on Android’s New Sideloading Restrictions!

Google will simplify sideloading for experienced Android users, allowing them to install unverified apps with an “advanced flow” that includes risk warnings. This follows backlash against new restrictions limiting such installations. The change aims to enhance safety while allowing user choice. Developer verification will also become mandatory to combat scams, but a lower barrier account type will be available for hobbyists.

https://www.androidauthority.com/android-power-users-install-unverified-apps-3615310/

DanaBot Malware Is Back to Infecting Windows After 6-month Break

DanaBot malware returns after 6-month hiatus, with version 669 using Tor for command-and-control. It's a banking trojan evolved into an info stealer, disrupted by law enforcement in May but now active again. It targets credentials and cryptocurrency data via nefarious emails and malvertising. Organizations can mitigate risks by updating security tools and blocking new threats identified by Zscaler.

https://www.bleepingcomputer.com/news/security/danabot-malware-is-back-to-infecting-windows-after-6-month-break/

How Massive Data Breaches Flood Illicit Markets While Personal Information Fuels Cybercrime Economy

Massive data breaches expose sensitive personal information, fueling a cybercrime economy where stolen data is sold for illicit purposes. Criminals exploit breaches from various targets, leading to identity theft and fraud. The sheer volume of stolen data creates a market for scammers, with various vendors and platforms facilitating sales, often using cryptocurrencies for transactions. As demand grows, so do data breaches, making the issue persistent and profitable for cybercriminals.

https://www.milwaukeeindependent.com/syndicated/massive-data-breaches-flood-illicit-markets-personal-information-fuels-cybercrime-economy/

GootLoader Is Back, Using a New Font Trick to Hide Malware on WordPress Sites

GootLoader malware has resurfaced, utilizing custom fonts to obscure filenames on WordPress sites, complicating detection. It exploits SEO tactics and comment endpoints to deliver encrypted payloads, often leading to domain controller compromises. The malware has evolved to disguise its true nature, using deceptive techniques to evade automated analysis and remains tied to a broader cybercriminal ecosystem involving various threat actors.

https://thehackernews.com/2025/11/gootloader-is-back-using-new-font-trick.html

Quantum Route Redirect PhaaS Targets Microsoft 365 Users Worldwide

Quantum Route Redirect, a new phishing automation platform, uses around 1,000 domains to steal Microsoft 365 credentials, primarily targeting users in the U.S. It automates phishing attacks by routing victims to malicious sites through deceptive emails. The kit is designed for ease of use, even for less skilled attackers, and incorporates mechanisms to evade detection by automated security tools. Security analysts recommend implementing robust URL filtering to combat this threat.

https://www.bleepingcomputer.com/news/security/quantum-route-redirect-phaas-targets-microsoft-365-users-worldwide/

GlassWorm Malware Discovered in Three VS Code Extensions With Thousands of Installs

GlassWorm Malware targets VS Code via three malicious extensions, harvesting credentials and using invisible code to spread. Despite attempts to remove it, the campaign persists, affecting various regions, including government entities. The malware showcases evolving attack techniques, such as utilizing blockchain for command/control. Security researchers identified a Russian-speaking attacker behind it, indicating significant risks to organizations using affected tools.

https://thehackernews.com/2025/11/glassworm-malware-discovered-in-three.html

Scroll to Top